CVE-2024-28108 (GCVE-0-2024-28108)
Vulnerability from cvelistv5 – Published: 2024-03-25 18:52 – Updated: 2024-08-02 00:48| URL | Tags |
|---|---|
| https://github.com/thorsten/phpMyFAQ/security/adv… | x_refsource_CONFIRM |
| https://github.com/thorsten/phpMyFAQ/commit/4fed1… | x_refsource_MISC |
{
  "containers": {
    "adp": [
      {
        "affected": [
          {
            "cpes": [
              "cpe:2.3:a:thorsten:phpmyfaq:*:*:*:*:*:*:*:*"
            ],
            "defaultStatus": "unknown",
            "product": "phpmyfaq",
            "vendor": "thorsten",
            "versions": [
              {
                "lessThan": "3.2.6",
                "status": "affected",
                "version": "3.2.5",
                "versionType": "custom"
              }
            ]
          }
        ],
        "metrics": [
          {
            "other": {
              "content": {
                "id": "CVE-2024-28108",
                "options": [
                  {
                    "Exploitation": "poc"
                  },
                  {
                    "Automatable": "no"
                  },
                  {
                    "Technical Impact": "partial"
                  }
                ],
                "role": "CISA Coordinator",
                "timestamp": "2024-08-01T18:41:12.256056Z",
                "version": "2.0.3"
              },
              "type": "ssvc"
            }
          }
        ],
        "providerMetadata": {
          "dateUpdated": "2024-08-01T18:50:13.531Z",
          "orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
          "shortName": "CISA-ADP"
        },
        "title": "CISA ADP Vulnrichment"
      },
      {
        "providerMetadata": {
          "dateUpdated": "2024-08-02T00:48:48.813Z",
          "orgId": "af854a3a-2127-422b-91ae-364da2661108",
          "shortName": "CVE"
        },
        "references": [
          {
            "name": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh",
            "tags": [
              "x_refsource_CONFIRM",
              "x_transferred"
            ],
            "url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh"
          },
          {
            "name": "https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634",
            "tags": [
              "x_refsource_MISC",
              "x_transferred"
            ],
            "url": "https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634"
          }
        ],
        "title": "CVE Program Container"
      }
    ],
    "cna": {
      "affected": [
        {
          "product": "phpMyFAQ",
          "vendor": "thorsten",
          "versions": [
            {
              "status": "affected",
              "version": "3.2.5"
            }
          ]
        }
      ],
      "descriptions": [
        {
          "lang": "en",
          "value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. Due to insufficient validation on the `contentLink` parameter, it is possible for unauthenticated users to inject HTML code to the page which might affect other users. _Also, requires that adding new FAQs is allowed for guests and that the admin doesn\u0027t check the content of a newly added FAQ._ This vulnerability is fixed in 3.2.6."
        }
      ],
      "metrics": [
        {
          "cvssV3_1": {
            "attackComplexity": "HIGH",
            "attackVector": "NETWORK",
            "availabilityImpact": "NONE",
            "baseScore": 4.7,
            "baseSeverity": "MEDIUM",
            "confidentialityImpact": "LOW",
            "integrityImpact": "LOW",
            "privilegesRequired": "NONE",
            "scope": "CHANGED",
            "userInteraction": "REQUIRED",
            "vectorString": "CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:C/C:L/I:L/A:N",
            "version": "3.1"
          }
        }
      ],
      "problemTypes": [
        {
          "descriptions": [
            {
              "cweId": "CWE-79",
              "description": "CWE-79: Improper Neutralization of Input During Web Page Generation (\u0027Cross-site Scripting\u0027)",
              "lang": "en",
              "type": "CWE"
            }
          ]
        },
        {
          "descriptions": [
            {
              "cweId": "CWE-80",
              "description": "CWE-80: Improper Neutralization of Script-Related HTML Tags in a Web Page (Basic XSS)",
              "lang": "en",
              "type": "CWE"
            }
          ]
        }
      ],
      "providerMetadata": {
        "dateUpdated": "2024-03-25T18:52:19.325Z",
        "orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
        "shortName": "GitHub_M"
      },
      "references": [
        {
          "name": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh",
          "tags": [
            "x_refsource_CONFIRM"
          ],
          "url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh"
        },
        {
          "name": "https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634",
          "tags": [
            "x_refsource_MISC"
          ],
          "url": "https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634"
        }
      ],
      "source": {
        "advisory": "GHSA-48vw-jpf8-hwqh",
        "discovery": "UNKNOWN"
      },
      "title": "phpMyFAQ Stored HTML Injection at contentLink"
    }
  },
  "cveMetadata": {
    "assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
    "assignerShortName": "GitHub_M",
    "cveId": "CVE-2024-28108",
    "datePublished": "2024-03-25T18:52:19.325Z",
    "dateReserved": "2024-03-04T14:19:14.059Z",
    "dateUpdated": "2024-08-02T00:48:48.813Z",
    "state": "PUBLISHED"
  },
  "dataType": "CVE_RECORD",
  "dataVersion": "5.1",
  "vulnerability-lookup:meta": {
    "epss": {
      "cve": "CVE-2024-28108",
      "date": "2026-09-16",
      "epss": "0.00539",
      "percentile": "0.44016"
    },
    "fkie_nvd": {
      "configurations": "[{\"nodes\": [{\"operator\": \"OR\", \"negate\": false, \"cpeMatch\": [{\"vulnerable\": true, \"criteria\": \"cpe:2.3:a:phpmyfaq:phpmyfaq:3.2.5:*:*:*:*:*:*:*\", \"matchCriteriaId\": \"99BD7923-9316-46E2-B3C4-33105AD9E901\"}]}]}]",
      "descriptions": "[{\"lang\": \"en\", \"value\": \"phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. Due to insufficient validation on the `contentLink` parameter, it is possible for unauthenticated users to inject HTML code to the page which might affect other users. _Also, requires that adding new FAQs is allowed for guests and that the admin doesn\u0027t check the content of a newly added FAQ._ This vulnerability is fixed in 3.2.6.\"}, {\"lang\": \"es\", \"value\": \"phpMyFAQ es una aplicaci\\u00f3n web de preguntas frecuentes de c\\u00f3digo abierto para PHP 8.1+ y MySQL, PostgreSQL y otras bases de datos. Debido a una validaci\\u00f3n insuficiente del par\\u00e1metro \\\"contentLink\\\", es posible que usuarios no autenticados inyecten c\\u00f3digo HTML en la p\\u00e1gina, lo que podr\\u00eda afectar a otros usuarios. _Adem\\u00e1s, requiere que se permita agregar nuevas preguntas frecuentes a los invitados y que el administrador no verifique el contenido de las preguntas frecuentes reci\\u00e9n agregadas._ Esta vulnerabilidad se corrigi\\u00f3 en 3.2.6.\"}]",
      "id": "CVE-2024-28108",
      "lastModified": "2025-01-09T17:00:12.770",
      "metrics": "{\"cvssMetricV31\": [{\"source\": \"security-advisories@github.com\", \"type\": \"Secondary\", \"cvssData\": {\"version\": \"3.1\", \"vectorString\": \"CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:C/C:L/I:L/A:N\", \"baseScore\": 4.7, \"baseSeverity\": \"MEDIUM\", \"attackVector\": \"NETWORK\", \"attackComplexity\": \"HIGH\", \"privilegesRequired\": \"NONE\", \"userInteraction\": \"REQUIRED\", \"scope\": \"CHANGED\", \"confidentialityImpact\": \"LOW\", \"integrityImpact\": \"LOW\", \"availabilityImpact\": \"NONE\"}, \"exploitabilityScore\": 1.6, \"impactScore\": 2.7}, {\"source\": \"nvd@nist.gov\", \"type\": \"Primary\", \"cvssData\": {\"version\": \"3.1\", \"vectorString\": \"CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N\", \"baseScore\": 6.1, \"baseSeverity\": \"MEDIUM\", \"attackVector\": \"NETWORK\", \"attackComplexity\": \"LOW\", \"privilegesRequired\": \"NONE\", \"userInteraction\": \"REQUIRED\", \"scope\": \"CHANGED\", \"confidentialityImpact\": \"LOW\", \"integrityImpact\": \"LOW\", \"availabilityImpact\": \"NONE\"}, \"exploitabilityScore\": 2.8, \"impactScore\": 2.7}]}",
      "published": "2024-03-25T19:15:58.700",
      "references": "[{\"url\": \"https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634\", \"source\": \"security-advisories@github.com\", \"tags\": [\"Patch\"]}, {\"url\": \"https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh\", \"source\": \"security-advisories@github.com\", \"tags\": [\"Exploit\", \"Vendor Advisory\"]}, {\"url\": \"https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634\", \"source\": \"af854a3a-2127-422b-91ae-364da2661108\", \"tags\": [\"Patch\"]}, {\"url\": \"https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh\", \"source\": \"af854a3a-2127-422b-91ae-364da2661108\", \"tags\": [\"Exploit\", \"Vendor Advisory\"]}]",
      "sourceIdentifier": "security-advisories@github.com",
      "vulnStatus": "Analyzed",
      "weaknesses": "[{\"source\": \"security-advisories@github.com\", \"type\": \"Secondary\", \"description\": [{\"lang\": \"en\", \"value\": \"CWE-79\"}, {\"lang\": \"en\", \"value\": \"CWE-80\"}]}, {\"source\": \"nvd@nist.gov\", \"type\": \"Primary\", \"description\": [{\"lang\": \"en\", \"value\": \"CWE-79\"}]}]"
    },
    "nvd": "{\"cve\":{\"id\":\"CVE-2024-28108\",\"sourceIdentifier\":\"security-advisories@github.com\",\"published\":\"2024-03-25T19:15:58.700\",\"lastModified\":\"2026-06-17T07:20:59.007\",\"vulnStatus\":\"Analyzed\",\"cveTags\":[],\"descriptions\":[{\"lang\":\"en\",\"value\":\"phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. Due to insufficient validation on the `contentLink` parameter, it is possible for unauthenticated users to inject HTML code to the page which might affect other users. _Also, requires that adding new FAQs is allowed for guests and that the admin doesn\u0027t check the content of a newly added FAQ._ This vulnerability is fixed in 3.2.6.\"},{\"lang\":\"es\",\"value\":\"phpMyFAQ es una aplicaci\u00f3n web de preguntas frecuentes de c\u00f3digo abierto para PHP 8.1+ y MySQL, PostgreSQL y otras bases de datos. Debido a una validaci\u00f3n insuficiente del par\u00e1metro \\\"contentLink\\\", es posible que usuarios no autenticados inyecten c\u00f3digo HTML en la p\u00e1gina, lo que podr\u00eda afectar a otros usuarios. _Adem\u00e1s, requiere que se permita agregar nuevas preguntas frecuentes a los invitados y que el administrador no verifique el contenido de las preguntas frecuentes reci\u00e9n agregadas._ Esta vulnerabilidad se corrigi\u00f3 en 3.2.6.\"}],\"affected\":[{\"source\":\"security-advisories@github.com\",\"affectedData\":[{\"vendor\":\"thorsten\",\"product\":\"phpMyFAQ\",\"versions\":[{\"version\":\"3.2.5\",\"status\":\"affected\"}]}]},{\"source\":\"134c704f-9b21-4f2e-91b3-4a467353bcc0\",\"affectedData\":[{\"vendor\":\"thorsten\",\"product\":\"phpmyfaq\",\"defaultStatus\":\"unknown\",\"cpes\":[\"cpe:2.3:a:thorsten:phpmyfaq:*:*:*:*:*:*:*:*\"],\"versions\":[{\"version\":\"3.2.5\",\"lessThan\":\"3.2.6\",\"versionType\":\"custom\",\"status\":\"affected\"}]}]}],\"metrics\":{\"cvssMetricV31\":[{\"source\":\"security-advisories@github.com\",\"type\":\"Secondary\",\"cvssData\":{\"version\":\"3.1\",\"vectorString\":\"CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:C/C:L/I:L/A:N\",\"baseScore\":4.7,\"baseSeverity\":\"MEDIUM\",\"attackVector\":\"NETWORK\",\"attackComplexity\":\"HIGH\",\"privilegesRequired\":\"NONE\",\"userInteraction\":\"REQUIRED\",\"scope\":\"CHANGED\",\"confidentialityImpact\":\"LOW\",\"integrityImpact\":\"LOW\",\"availabilityImpact\":\"NONE\"},\"exploitabilityScore\":1.6,\"impactScore\":2.7},{\"source\":\"nvd@nist.gov\",\"type\":\"Primary\",\"cvssData\":{\"version\":\"3.1\",\"vectorString\":\"CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N\",\"baseScore\":6.1,\"baseSeverity\":\"MEDIUM\",\"attackVector\":\"NETWORK\",\"attackComplexity\":\"LOW\",\"privilegesRequired\":\"NONE\",\"userInteraction\":\"REQUIRED\",\"scope\":\"CHANGED\",\"confidentialityImpact\":\"LOW\",\"integrityImpact\":\"LOW\",\"availabilityImpact\":\"NONE\"},\"exploitabilityScore\":2.8,\"impactScore\":2.7}],\"ssvcV203\":[{\"source\":\"134c704f-9b21-4f2e-91b3-4a467353bcc0\",\"ssvcData\":{\"timestamp\":\"2024-08-01T18:41:12.256056Z\",\"id\":\"CVE-2024-28108\",\"options\":[{\"exploitation\":\"poc\"},{\"automatable\":\"no\"},{\"technicalImpact\":\"partial\"}],\"role\":\"CISA Coordinator\",\"version\":\"2.0.3\"}}]},\"weaknesses\":[{\"source\":\"security-advisories@github.com\",\"type\":\"Secondary\",\"description\":[{\"lang\":\"en\",\"value\":\"CWE-79\"},{\"lang\":\"en\",\"value\":\"CWE-80\"}]},{\"source\":\"nvd@nist.gov\",\"type\":\"Primary\",\"description\":[{\"lang\":\"en\",\"value\":\"CWE-79\"}]}],\"configurations\":[{\"nodes\":[{\"operator\":\"OR\",\"negate\":false,\"cpeMatch\":[{\"vulnerable\":true,\"criteria\":\"cpe:2.3:a:phpmyfaq:phpmyfaq:3.2.5:*:*:*:*:*:*:*\",\"matchCriteriaId\":\"99BD7923-9316-46E2-B3C4-33105AD9E901\"}]}]}],\"references\":[{\"url\":\"https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634\",\"source\":\"security-advisories@github.com\",\"tags\":[\"Patch\"]},{\"url\":\"https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh\",\"source\":\"security-advisories@github.com\",\"tags\":[\"Exploit\",\"Vendor Advisory\"]},{\"url\":\"https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634\",\"source\":\"af854a3a-2127-422b-91ae-364da2661108\",\"tags\":[\"Patch\"]},{\"url\":\"https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh\",\"source\":\"af854a3a-2127-422b-91ae-364da2661108\",\"tags\":[\"Exploit\",\"Vendor Advisory\"]}]}}",
    "redhat_vex": {
      "current_release_date": "2025-05-28T19:10:27+00:00",
      "cve": "CVE-2024-28108",
      "id": "CVE-2024-28108",
      "initial_release_date": "2024-01-01T00:00:00+00:00",
      "product_status:known_not_affected": "1",
      "source": "Red Hat CSAF VEX",
      "status": "final",
      "title": "phpMyFAQ Stored HTML Injection at contentLink",
      "url": "https://security.access.redhat.com/data/csaf/v2/vex/2024/cve-2024-28108.json",
      "version": "3"
    },
    "vulnrichment": {
      "containers": "{\"adp\": [{\"title\": \"CISA ADP Vulnrichment\", \"metrics\": [{\"other\": {\"type\": \"ssvc\", \"content\": {\"id\": \"CVE-2024-28108\", \"role\": \"CISA Coordinator\", \"options\": [{\"Exploitation\": \"poc\"}, {\"Automatable\": \"no\"}, {\"Technical Impact\": \"partial\"}], \"version\": \"2.0.3\", \"timestamp\": \"2024-08-01T18:41:12.256056Z\"}}}], \"affected\": [{\"cpes\": [\"cpe:2.3:a:thorsten:phpmyfaq:*:*:*:*:*:*:*:*\"], \"vendor\": \"thorsten\", \"product\": \"phpmyfaq\", \"versions\": [{\"status\": \"affected\", \"version\": \"3.2.5\", \"lessThan\": \"3.2.6\", \"versionType\": \"custom\"}], \"defaultStatus\": \"unknown\"}], \"providerMetadata\": {\"orgId\": \"134c704f-9b21-4f2e-91b3-4a467353bcc0\", \"shortName\": \"CISA-ADP\", \"dateUpdated\": \"2024-08-01T18:42:05.001Z\"}}], \"cna\": {\"title\": \"phpMyFAQ Stored HTML Injection at contentLink\", \"source\": {\"advisory\": \"GHSA-48vw-jpf8-hwqh\", \"discovery\": \"UNKNOWN\"}, \"metrics\": [{\"cvssV3_1\": {\"scope\": \"CHANGED\", \"version\": \"3.1\", \"baseScore\": 4.7, \"attackVector\": \"NETWORK\", \"baseSeverity\": \"MEDIUM\", \"vectorString\": \"CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:C/C:L/I:L/A:N\", \"integrityImpact\": \"LOW\", \"userInteraction\": \"REQUIRED\", \"attackComplexity\": \"HIGH\", \"availabilityImpact\": \"NONE\", \"privilegesRequired\": \"NONE\", \"confidentialityImpact\": \"LOW\"}}], \"affected\": [{\"vendor\": \"thorsten\", \"product\": \"phpMyFAQ\", \"versions\": [{\"status\": \"affected\", \"version\": \"3.2.5\"}]}], \"references\": [{\"url\": \"https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh\", \"name\": \"https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh\", \"tags\": [\"x_refsource_CONFIRM\"]}, {\"url\": \"https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634\", \"name\": \"https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634\", \"tags\": [\"x_refsource_MISC\"]}], \"descriptions\": [{\"lang\": \"en\", \"value\": \"phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. Due to insufficient validation on the `contentLink` parameter, it is possible for unauthenticated users to inject HTML code to the page which might affect other users. _Also, requires that adding new FAQs is allowed for guests and that the admin doesn\u0027t check the content of a newly added FAQ._ This vulnerability is fixed in 3.2.6.\"}], \"problemTypes\": [{\"descriptions\": [{\"lang\": \"en\", \"type\": \"CWE\", \"cweId\": \"CWE-79\", \"description\": \"CWE-79: Improper Neutralization of Input During Web Page Generation (\u0027Cross-site Scripting\u0027)\"}]}, {\"descriptions\": [{\"lang\": \"en\", \"type\": \"CWE\", \"cweId\": \"CWE-80\", \"description\": \"CWE-80: Improper Neutralization of Script-Related HTML Tags in a Web Page (Basic XSS)\"}]}], \"providerMetadata\": {\"orgId\": \"a0819718-46f1-4df5-94e2-005712e83aaa\", \"shortName\": \"GitHub_M\", \"dateUpdated\": \"2024-03-25T18:52:19.325Z\"}}}",
      "cveMetadata": "{\"cveId\": \"CVE-2024-28108\", \"state\": \"PUBLISHED\", \"dateUpdated\": \"2024-08-01T18:50:13.531Z\", \"dateReserved\": \"2024-03-04T14:19:14.059Z\", \"assignerOrgId\": \"a0819718-46f1-4df5-94e2-005712e83aaa\", \"datePublished\": \"2024-03-25T18:52:19.325Z\", \"assignerShortName\": \"GitHub_M\"}",
      "dataType": "CVE_RECORD",
      "dataVersion": "5.1"
    }
  }
}
BDU:2024-02336 (CVE-2024-28108)
Vulnerability from fstec – Published: 2024-03-27 – Updated: 2024-03-27 – View on bdu.fstec.ru Exploit publicly available Fixed{
"CVSS 2.0": "AV:N/AC:H/Au:N/C:P/I:P/A:N",
"CVSS 3.0": "AV:N/AC:H/PR:N/UI:R/S:C/C:L/I:L/A:N",
"CVSS 4.0": null,
"remediation_\u0418\u0434\u0435\u043d\u0442\u0438\u0444\u0438\u043a\u0430\u0442\u043e\u0440": null,
"remediation_\u041d\u0430\u0438\u043c\u0435\u043d\u043e\u0432\u0430\u043d\u0438\u0435": null,
"\u0412\u0435\u043d\u0434\u043e\u0440 \u041f\u041e": "\u0421\u043e\u043e\u0431\u0449\u0435\u0441\u0442\u0432\u043e \u0441\u0432\u043e\u0431\u043e\u0434\u043d\u043e\u0433\u043e \u043f\u0440\u043e\u0433\u0440\u0430\u043c\u043c\u043d\u043e\u0433\u043e \u043e\u0431\u0435\u0441\u043f\u0435\u0447\u0435\u043d\u0438\u044f",
"\u0412\u0435\u0440\u0441\u0438\u044f \u041f\u041e": "\u043e\u0442 3.2.5 \u0434\u043e 3.2.6 (phpMyFAQ)",
"\u0412\u043e\u0437\u043c\u043e\u0436\u043d\u044b\u0435 \u043c\u0435\u0440\u044b \u043f\u043e \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0438\u044e": "\u0418\u0441\u043f\u043e\u043b\u044c\u0437\u043e\u0432\u0430\u043d\u0438\u0435 \u0440\u0435\u043a\u043e\u043c\u0435\u043d\u0434\u0430\u0446\u0438\u0439:\nhttps://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh",
"\u0414\u0430\u0442\u0430 \u0432\u044b\u044f\u0432\u043b\u0435\u043d\u0438\u044f": "25.03.2024",
"\u0414\u0430\u0442\u0430 \u043f\u043e\u0441\u043b\u0435\u0434\u043d\u0435\u0433\u043e \u043e\u0431\u043d\u043e\u0432\u043b\u0435\u043d\u0438\u044f": "27.03.2024",
"\u0414\u0430\u0442\u0430 \u043f\u0443\u0431\u043b\u0438\u043a\u0430\u0446\u0438\u0438": "27.03.2024",
"\u0418\u0434\u0435\u043d\u0442\u0438\u0444\u0438\u043a\u0430\u0442\u043e\u0440": "BDU:2024-02336",
"\u0418\u0434\u0435\u043d\u0442\u0438\u0444\u0438\u043a\u0430\u0442\u043e\u0440\u044b \u0434\u0440\u0443\u0433\u0438\u0445 \u0441\u0438\u0441\u0442\u0435\u043c \u043e\u043f\u0438\u0441\u0430\u043d\u0438\u0439 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "CVE-2024-28108",
"\u0418\u043d\u0444\u043e\u0440\u043c\u0430\u0446\u0438\u044f \u043e\u0431 \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0438\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0430",
"\u041a\u043b\u0430\u0441\u0441 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u043a\u043e\u0434\u0430",
"\u041d\u0430\u0437\u0432\u0430\u043d\u0438\u0435 \u041f\u041e": "phpMyFAQ",
"\u041d\u0430\u0438\u043c\u0435\u043d\u043e\u0432\u0430\u043d\u0438\u0435 \u041e\u0421 \u0438 \u0442\u0438\u043f \u0430\u043f\u043f\u0430\u0440\u0430\u0442\u043d\u043e\u0439 \u043f\u043b\u0430\u0442\u0444\u043e\u0440\u043c\u044b": null,
"\u041d\u0430\u0438\u043c\u0435\u043d\u043e\u0432\u0430\u043d\u0438\u0435 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u043f\u0430\u0440\u0430\u043c\u0435\u0442\u0440\u0430 contentLink \u0432\u0435\u0431-\u043f\u0440\u0438\u043b\u043e\u0436\u0435\u043d\u0438\u044f phpMyFAQ, \u043f\u043e\u0437\u0432\u043e\u043b\u044f\u044e\u0449\u0430\u044f \u043d\u0430\u0440\u0443\u0448\u0438\u0442\u0435\u043b\u044e \u043f\u0440\u043e\u0432\u043e\u0434\u0438\u0442\u044c \u043c\u0435\u0436\u0441\u0430\u0439\u0442\u043e\u0432\u044b\u0435 \u0441\u0446\u0435\u043d\u0430\u0440\u043d\u044b\u0435 \u0430\u0442\u0430\u043a\u0438 (XSS)",
"\u041d\u0430\u043b\u0438\u0447\u0438\u0435 \u044d\u043a\u0441\u043f\u043b\u043e\u0439\u0442\u0430": "\u0421\u0443\u0449\u0435\u0441\u0442\u0432\u0443\u0435\u0442 \u0432 \u043e\u0442\u043a\u0440\u044b\u0442\u043e\u043c \u0434\u043e\u0441\u0442\u0443\u043f\u0435",
"\u041e\u043f\u0438\u0441\u0430\u043d\u0438\u0435 \u043e\u0448\u0438\u0431\u043a\u0438 CWE": "\u041d\u0435\u043f\u0440\u0438\u043d\u044f\u0442\u0438\u0435 \u043c\u0435\u0440 \u043f\u043e \u0437\u0430\u0449\u0438\u0442\u0435 \u0441\u0442\u0440\u0443\u043a\u0442\u0443\u0440\u044b \u0432\u0435\u0431-\u0441\u0442\u0440\u0430\u043d\u0438\u0446\u044b (\u0438\u043b\u0438 \\\u00ab\u041c\u0435\u0436\u0441\u0430\u0439\u0442\u043e\u0432\u0430\u044f \u0441\u0446\u0435\u043d\u0430\u0440\u043d\u0430\u044f \u0430\u0442\u0430\u043a\u0430\\\u00bb) (CWE-79), \u041d\u0435\u043f\u0440\u0438\u043d\u044f\u0442\u0438\u0435 \u043c\u0435\u0440 \u043f\u043e \u043d\u0435\u0439\u0442\u0440\u0430\u043b\u0438\u0437\u0430\u0446\u0438\u0438 script-related \u0442\u044d\u0433\u043e\u0432 HTML \u043d\u0430 \u0432\u0435\u0431-\u0441\u0442\u0440\u0430\u043d\u0438\u0446\u0435 (\u043e\u0441\u043d\u043e\u0432\u043d\u043e\u0439 XSS) (CWE-80)",
"\u041e\u043f\u0438\u0441\u0430\u043d\u0438\u0435 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0423\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u044c \u043f\u0430\u0440\u0430\u043c\u0435\u0442\u0440\u0430 contentLink \u0432\u0435\u0431-\u043f\u0440\u0438\u043b\u043e\u0436\u0435\u043d\u0438\u044f phpMyFAQ \u0441\u0432\u044f\u0437\u0430\u043d\u0430 \u0441 \u043d\u0435\u043f\u0440\u0438\u043d\u044f\u0442\u0438\u0435\u043c \u043c\u0435\u0440 \u043f\u043e \u0437\u0430\u0449\u0438\u0442\u0435 \u0441\u0442\u0440\u0443\u043a\u0442\u0443\u0440\u044b \u0432\u0435\u0431-\u0441\u0442\u0440\u0430\u043d\u0438\u0446\u044b. \u042d\u043a\u0441\u043f\u043b\u0443\u0430\u0442\u0430\u0446\u0438\u044f \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438 \u043c\u043e\u0436\u0435\u0442 \u043f\u043e\u0437\u0432\u043e\u043b\u0438\u0442\u044c \u043d\u0430\u0440\u0443\u0448\u0438\u0442\u0435\u043b\u044e, \u0434\u0435\u0439\u0441\u0442\u0432\u0443\u044e\u0449\u0435\u043c\u0443 \u0443\u0434\u0430\u043b\u0451\u043d\u043d\u043e, \u043f\u0440\u043e\u0432\u043e\u0434\u0438\u0442\u044c \u043c\u0435\u0436\u0441\u0430\u0439\u0442\u043e\u0432\u044b\u0435 \u0441\u0446\u0435\u043d\u0430\u0440\u043d\u044b\u0435 \u0430\u0442\u0430\u043a\u0438 (XSS) \u043f\u0443\u0442\u0435\u043c \u0432\u043d\u0435\u0434\u0440\u0435\u043d\u0438\u044f \u0432\u0440\u0435\u0434\u043e\u043d\u043e\u0441\u043d\u043e\u0433\u043e HTML-\u043a\u043e\u0434\u0430",
"\u041f\u043e\u0441\u043b\u0435\u0434\u0441\u0442\u0432\u0438\u044f \u044d\u043a\u0441\u043f\u043b\u0443\u0430\u0442\u0430\u0446\u0438\u0438 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": null,
"\u041f\u0440\u043e\u0447\u0430\u044f \u0438\u043d\u0444\u043e\u0440\u043c\u0430\u0446\u0438\u044f": null,
"\u0421\u0432\u044f\u0437\u044c \u0441 \u0438\u043d\u0446\u0438\u0434\u0435\u043d\u0442\u0430\u043c\u0438 \u0418\u0411": "\u0414\u0430\u043d\u043d\u044b\u0435 \u0443\u0442\u043e\u0447\u043d\u044f\u044e\u0442\u0441\u044f",
"\u0421\u043e\u0441\u0442\u043e\u044f\u043d\u0438\u0435 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u041e\u043f\u0443\u0431\u043b\u0438\u043a\u043e\u0432\u0430\u043d\u0430",
"\u0421\u043f\u043e\u0441\u043e\u0431 \u0443\u0441\u0442\u0440\u0430\u043d\u0435\u043d\u0438\u044f": "\u041e\u0431\u043d\u043e\u0432\u043b\u0435\u043d\u0438\u0435 \u043f\u0440\u043e\u0433\u0440\u0430\u043c\u043c\u043d\u043e\u0433\u043e \u043e\u0431\u0435\u0441\u043f\u0435\u0447\u0435\u043d\u0438\u044f",
"\u0421\u043f\u043e\u0441\u043e\u0431 \u044d\u043a\u0441\u043f\u043b\u0443\u0430\u0442\u0430\u0446\u0438\u0438": "\u0418\u043d\u044a\u0435\u043a\u0446\u0438\u044f",
"\u0421\u0441\u044b\u043b\u043a\u0438 \u043d\u0430 \u0438\u0441\u0442\u043e\u0447\u043d\u0438\u043a\u0438": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh\nhttps://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634\nhttps://vuldb.com/?id.257888",
"\u0421\u0442\u0430\u0442\u0443\u0441 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u041f\u043e\u0434\u0442\u0432\u0435\u0440\u0436\u0434\u0435\u043d\u0430 \u043f\u0440\u043e\u0438\u0437\u0432\u043e\u0434\u0438\u0442\u0435\u043b\u0435\u043c",
"\u0422\u0438\u043f \u041f\u041e": "\u041f\u0440\u0438\u043a\u043b\u0430\u0434\u043d\u043e\u0435 \u041f\u041e \u0438\u043d\u0444\u043e\u0440\u043c\u0430\u0446\u0438\u043e\u043d\u043d\u044b\u0445 \u0441\u0438\u0441\u0442\u0435\u043c",
"\u0422\u0438\u043f \u043e\u0448\u0438\u0431\u043a\u0438 CWE": "CWE-79, CWE-80",
"\u0423\u0440\u043e\u0432\u0435\u043d\u044c \u043e\u043f\u0430\u0441\u043d\u043e\u0441\u0442\u0438 \u0443\u044f\u0437\u0432\u0438\u043c\u043e\u0441\u0442\u0438": "\u0421\u0440\u0435\u0434\u043d\u0438\u0439 \u0443\u0440\u043e\u0432\u0435\u043d\u044c \u043e\u043f\u0430\u0441\u043d\u043e\u0441\u0442\u0438 (\u0431\u0430\u0437\u043e\u0432\u0430\u044f \u043e\u0446\u0435\u043d\u043a\u0430 CVSS 2.0 \u0441\u043e\u0441\u0442\u0430\u0432\u043b\u044f\u0435\u0442 4)\n\u0421\u0440\u0435\u0434\u043d\u0438\u0439 \u0443\u0440\u043e\u0432\u0435\u043d\u044c \u043e\u043f\u0430\u0441\u043d\u043e\u0441\u0442\u0438 (\u0431\u0430\u0437\u043e\u0432\u0430\u044f \u043e\u0446\u0435\u043d\u043a\u0430 CVSS 3.0 \u0441\u043e\u0441\u0442\u0430\u0432\u043b\u044f\u0435\u0442 4,7)"
}
FKIE_CVE-2024-28108
Vulnerability from fkie_nvd - Published: 2024-03-25 19:15 - Updated: 2026-06-17 07:206.1 (Medium) - CVSS:3.1/
{
  "affected": [
    {
      "affectedData": [
        {
          "product": "phpMyFAQ",
          "vendor": "thorsten",
          "versions": [
            {
              "status": "affected",
              "version": "3.2.5"
            }
          ]
        }
      ],
      "source": "security-advisories@github.com"
    },
    {
      "affectedData": [
        {
          "cpes": [
            "cpe:2.3:a:thorsten:phpmyfaq:*:*:*:*:*:*:*:*"
          ],
          "defaultStatus": "unknown",
          "product": "phpmyfaq",
          "vendor": "thorsten",
          "versions": [
            {
              "lessThan": "3.2.6",
              "status": "affected",
              "version": "3.2.5",
              "versionType": "custom"
            }
          ]
        }
      ],
      "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0"
    }
  ],
  "configurations": [
    {
      "nodes": [
        {
          "cpeMatch": [
            {
              "criteria": "cpe:2.3:a:phpmyfaq:phpmyfaq:3.2.5:*:*:*:*:*:*:*",
              "matchCriteriaId": "99BD7923-9316-46E2-B3C4-33105AD9E901",
              "vulnerable": true
            }
          ],
          "negate": false,
          "operator": "OR"
        }
      ]
    }
  ],
  "cveTags": [],
  "descriptions": [
    {
      "lang": "en",
      "value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. Due to insufficient validation on the `contentLink` parameter, it is possible for unauthenticated users to inject HTML code to the page which might affect other users. _Also, requires that adding new FAQs is allowed for guests and that the admin doesn\u0027t check the content of a newly added FAQ._ This vulnerability is fixed in 3.2.6."
    },
    {
      "lang": "es",
      "value": "phpMyFAQ es una aplicaci\u00f3n web de preguntas frecuentes de c\u00f3digo abierto para PHP 8.1+ y MySQL, PostgreSQL y otras bases de datos. Debido a una validaci\u00f3n insuficiente del par\u00e1metro \"contentLink\", es posible que usuarios no autenticados inyecten c\u00f3digo HTML en la p\u00e1gina, lo que podr\u00eda afectar a otros usuarios. _Adem\u00e1s, requiere que se permita agregar nuevas preguntas frecuentes a los invitados y que el administrador no verifique el contenido de las preguntas frecuentes reci\u00e9n agregadas._ Esta vulnerabilidad se corrigi\u00f3 en 3.2.6."
    }
  ],
  "id": "CVE-2024-28108",
  "lastModified": "2026-06-17T07:20:59.007",
  "metrics": {
    "cvssMetricV31": [
      {
        "cvssData": {
          "attackComplexity": "HIGH",
          "attackVector": "NETWORK",
          "availabilityImpact": "NONE",
          "baseScore": 4.7,
          "baseSeverity": "MEDIUM",
          "confidentialityImpact": "LOW",
          "integrityImpact": "LOW",
          "privilegesRequired": "NONE",
          "scope": "CHANGED",
          "userInteraction": "REQUIRED",
          "vectorString": "CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:C/C:L/I:L/A:N",
          "version": "3.1"
        },
        "exploitabilityScore": 1.6,
        "impactScore": 2.7,
        "source": "security-advisories@github.com",
        "type": "Secondary"
      },
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "NONE",
          "baseScore": 6.1,
          "baseSeverity": "MEDIUM",
          "confidentialityImpact": "LOW",
          "integrityImpact": "LOW",
          "privilegesRequired": "NONE",
          "scope": "CHANGED",
          "userInteraction": "REQUIRED",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N",
          "version": "3.1"
        },
        "exploitabilityScore": 2.8,
        "impactScore": 2.7,
        "source": "nvd@nist.gov",
        "type": "Primary"
      }
    ],
    "ssvcV203": [
      {
        "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
        "ssvcData": {
          "id": "CVE-2024-28108",
          "options": [
            {
              "exploitation": "poc"
            },
            {
              "automatable": "no"
            },
            {
              "technicalImpact": "partial"
            }
          ],
          "role": "CISA Coordinator",
          "timestamp": "2024-08-01T18:41:12.256056Z",
          "version": "2.0.3"
        }
      }
    ]
  },
  "published": "2024-03-25T19:15:58.700",
  "references": [
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Patch"
      ],
      "url": "https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634"
    },
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh"
    },
    {
      "source": "af854a3a-2127-422b-91ae-364da2661108",
      "tags": [
        "Patch"
      ],
      "url": "https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634"
    },
    {
      "source": "af854a3a-2127-422b-91ae-364da2661108",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh"
    }
  ],
  "sourceIdentifier": "security-advisories@github.com",
  "vulnStatus": "Analyzed",
  "weaknesses": [
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-79"
        },
        {
          "lang": "en",
          "value": "CWE-80"
        }
      ],
      "source": "security-advisories@github.com",
      "type": "Secondary"
    },
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-79"
        }
      ],
      "source": "nvd@nist.gov",
      "type": "Primary"
    }
  ]
}
GHSA-48VW-JPF8-HWQH
Vulnerability from github – Published: 2024-03-25 19:45 – Updated: 2024-03-25 22:31Summary
Due to insufficient validation on the contentLink parameter, it is possible for unauthenticated users to inject HTML code to the page which might affect other users. Also, requires that adding new FAQs is allowed for guests and that the admin doesn't check the content of a newly added FAQ.
PoC
-
Browse to ../phpmyfaq/index.php?action=add&cat=0 , enter
https://test.com?p=<h1>HTML_INJECTION</h1>for the contentLink parameter. -
Verify the HTML injection by viewing the FAQ itself, “All categories” → “CategoryName” → ”QuestionName”.
Impact
Attackers can manipulate the appearance and functionality of web pages by injecting malicious HTML code. This can lead to various undesirable outcomes, such as defacing the website, redirecting users to malicious sites, or altering the content to deceive users. Additionally, unauthenticated HTML injection can compromise user privacy by displaying sensitive information or misleading content. It undermines the integrity of the application and erodes user trust, potentially resulting in loss of reputation and credibility.
{
"affected": [
{
"package": {
"ecosystem": "Packagist",
"name": "phpmyfaq/phpmyfaq"
},
"ranges": [
{
"events": [
{
"introduced": "3.2.5"
},
{
"fixed": "3.2.6"
}
],
"type": "ECOSYSTEM"
}
],
"versions": [
"3.2.5"
]
}
],
"aliases": [
"CVE-2024-28108"
],
"database_specific": {
"cwe_ids": [
"CWE-79",
"CWE-80"
],
"github_reviewed": true,
"github_reviewed_at": "2024-03-25T19:45:23Z",
"nvd_published_at": "2024-03-25T19:15:58Z",
"severity": "MODERATE"
},
"details": "### Summary\nDue to insufficient validation on the `contentLink` parameter, it is possible for unauthenticated users to inject HTML code to the page which might affect other users. _Also, requires that adding new FAQs is allowed for guests and that the admin doesn\u0027t check the content of a newly added FAQ._\n\n### PoC\n1. Browse to ../phpmyfaq/index.php?action=add\u0026cat=0 , enter `https://test.com?p=\u003ch1\u003eHTML_INJECTION\u003c/h1\u003e` for the contentLink parameter.\n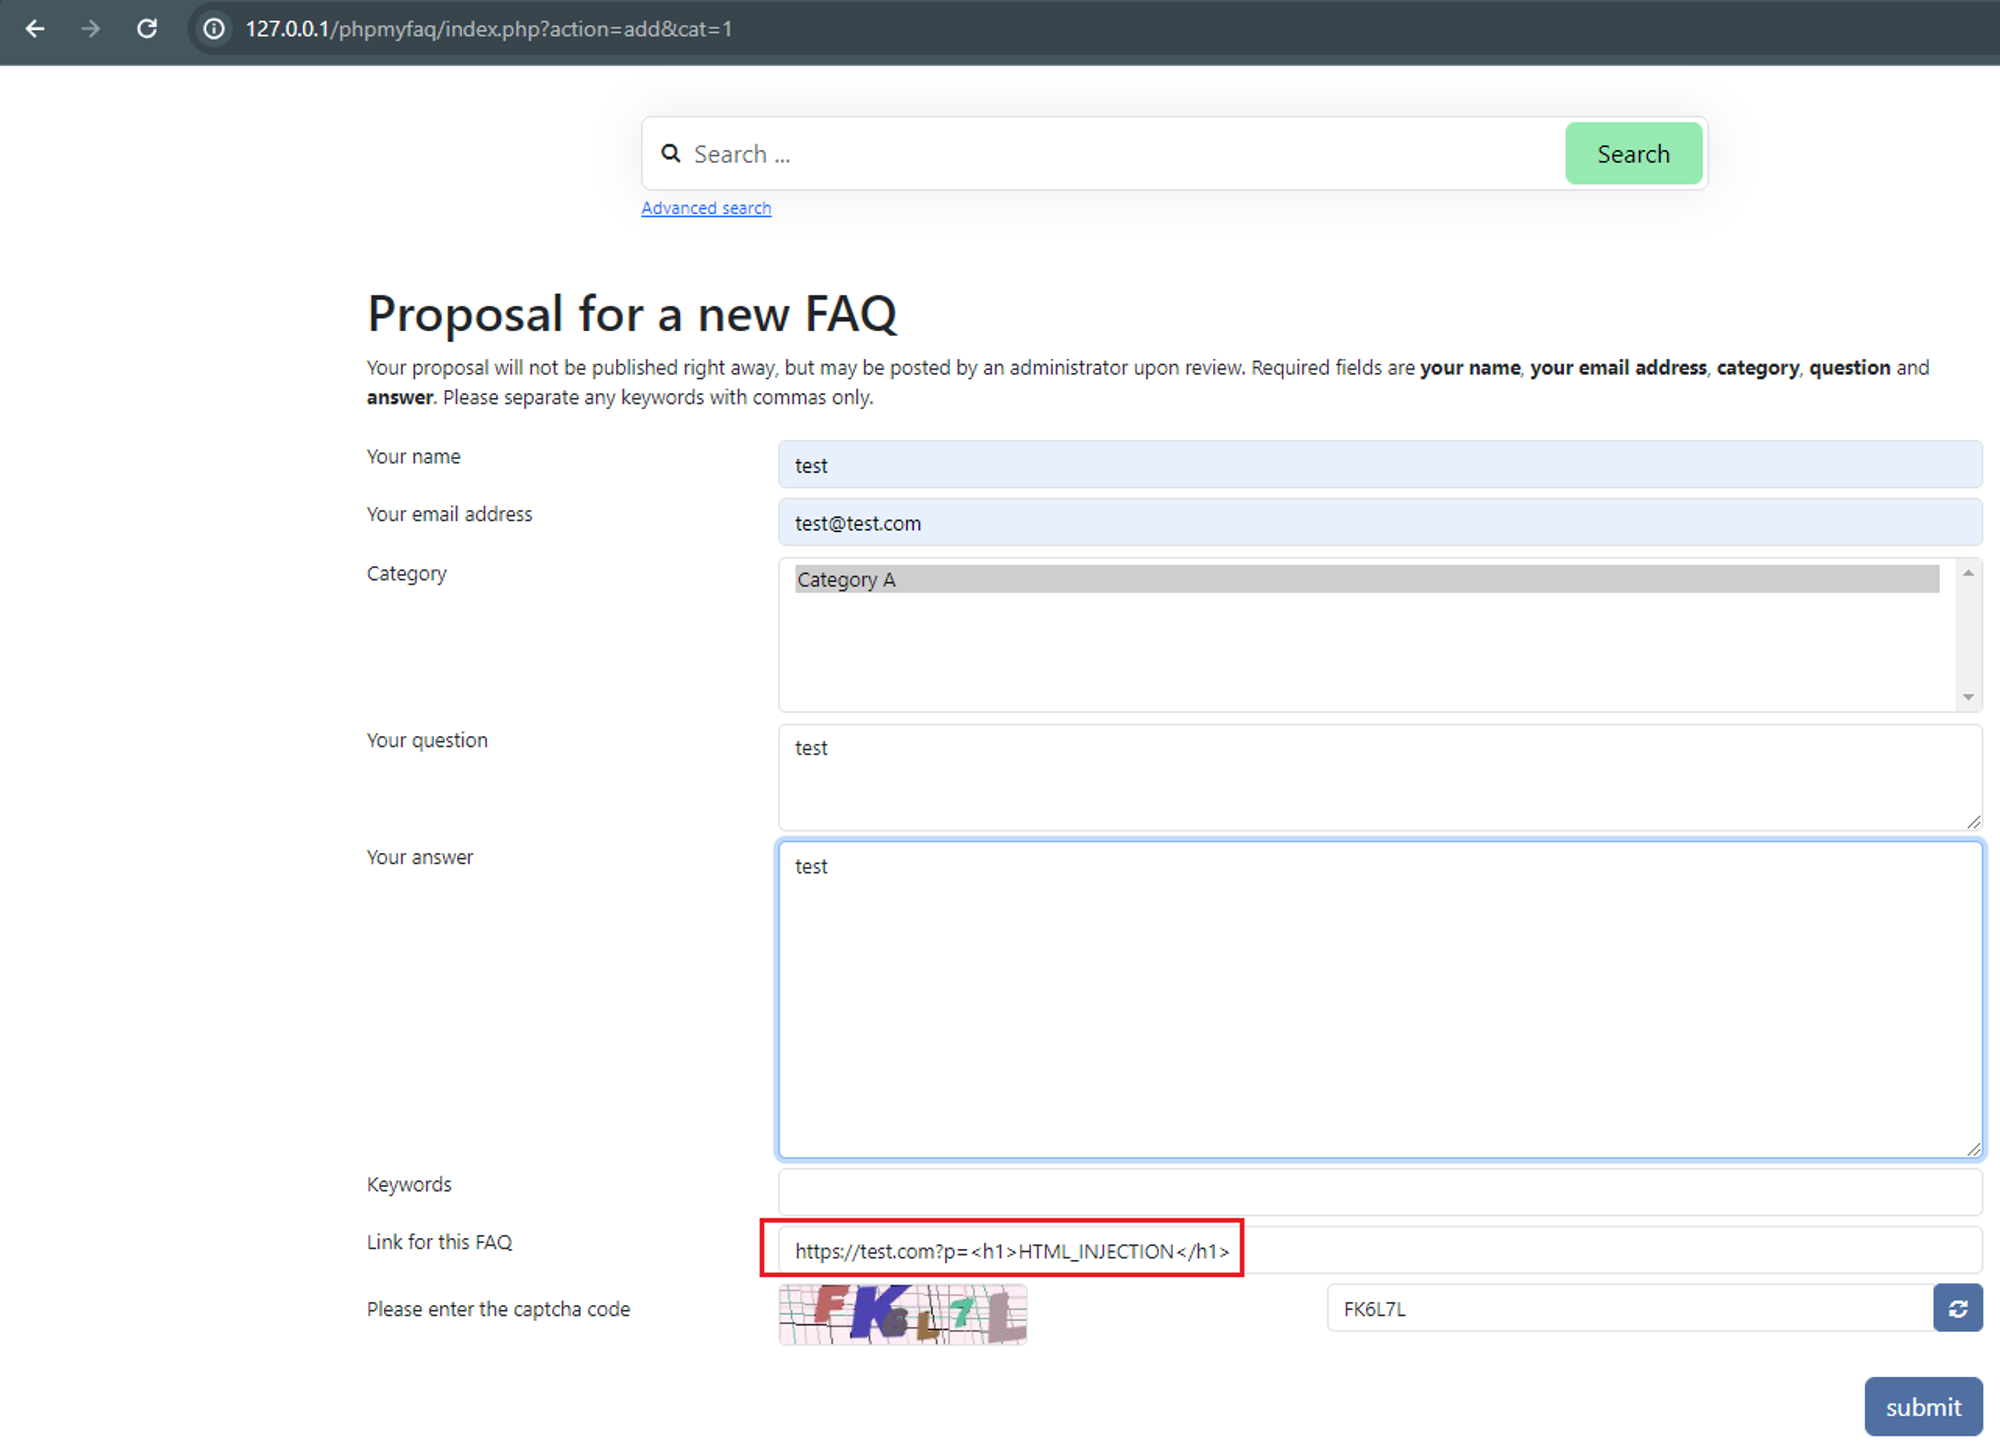\n\n2. Verify the HTML injection by viewing the FAQ itself, \u201cAll categories\u201d \u2192 \u201cCategoryName\u201d \u2192 \u201dQuestionName\u201d.\n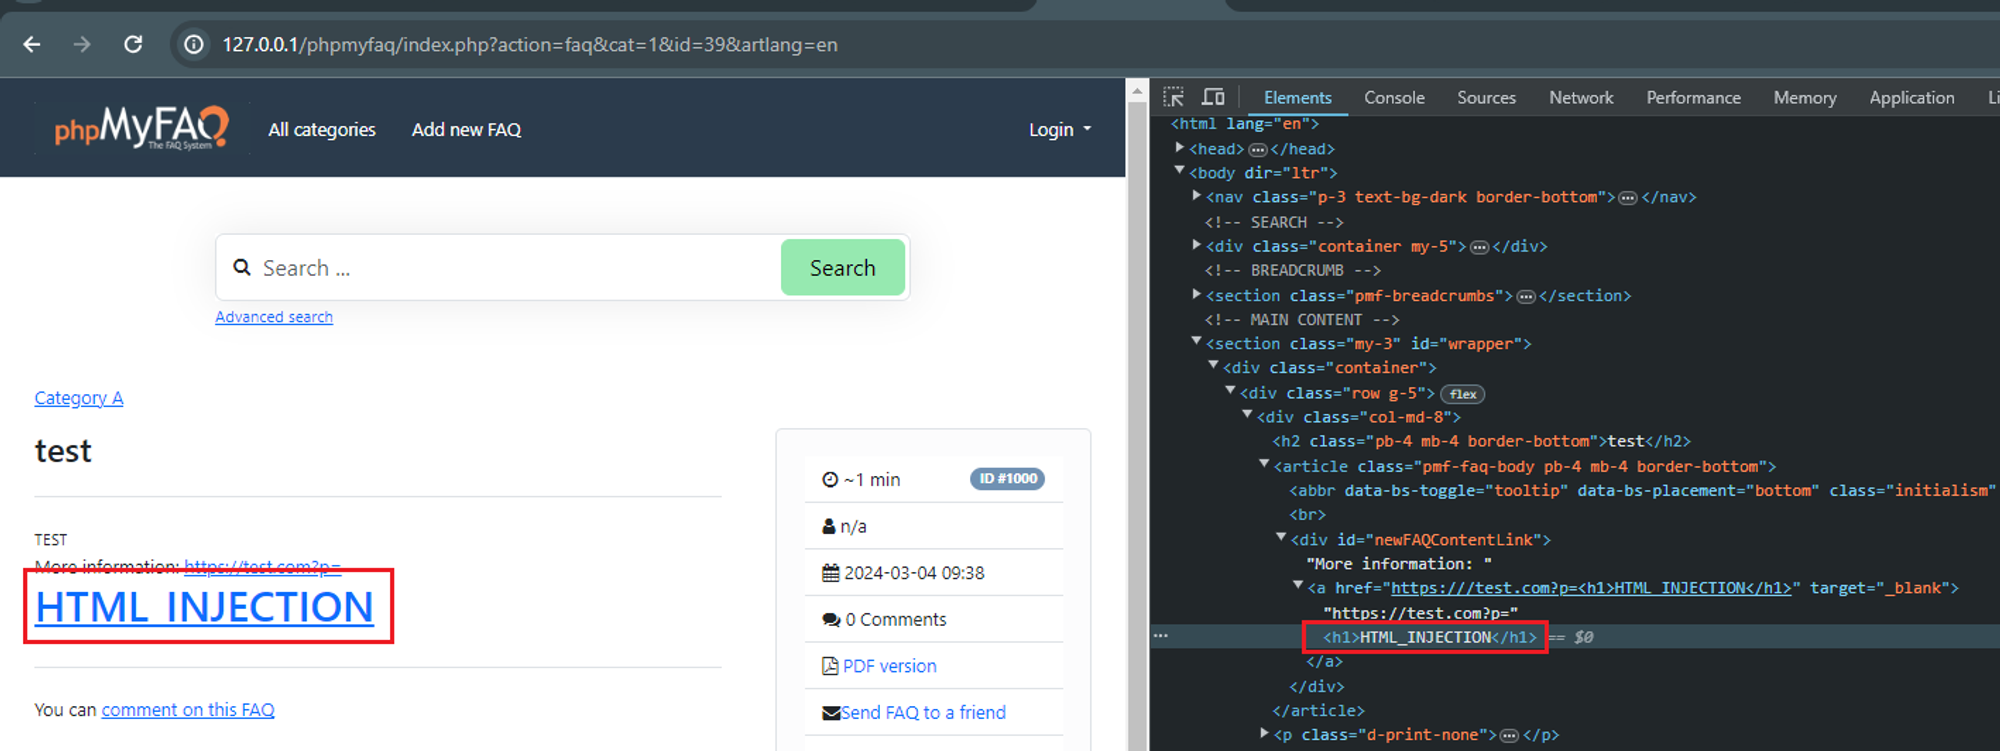\n\n### Impact\nAttackers can manipulate the appearance and functionality of web pages by injecting malicious HTML code. This can lead to various undesirable outcomes, such as defacing the website, redirecting users to malicious sites, or altering the content to deceive users. Additionally, unauthenticated HTML injection can compromise user privacy by displaying sensitive information or misleading content. It undermines the integrity of the application and erodes user trust, potentially resulting in loss of reputation and credibility. ",
"id": "GHSA-48vw-jpf8-hwqh",
"modified": "2024-03-25T22:31:35Z",
"published": "2024-03-25T19:45:23Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-28108"
},
{
"type": "WEB",
"url": "https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634"
},
{
"type": "PACKAGE",
"url": "https://github.com/thorsten/phpMyFAQ"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:L/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N",
"type": "CVSS_V3"
}
],
"summary": "phpMyFAQ Stored HTML Injection at contentLink"
}
GSD-2024-28108
Vulnerability from gsd - Updated: 2024-03-05 06:02{
"gsd": {
"metadata": {
"exploitCode": "unknown",
"remediation": "unknown",
"reportConfidence": "confirmed",
"type": "vulnerability"
},
"osvSchema": {
"aliases": [
"CVE-2024-28108"
],
"details": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. Due to insufficient validation on the `contentLink` parameter, it is possible for unauthenticated users to inject HTML code to the page which might affect other users. _Also, requires that adding new FAQs is allowed for guests and that the admin doesn\u0027t check the content of a newly added FAQ._ This vulnerability is fixed in 3.2.6.",
"id": "GSD-2024-28108",
"modified": "2024-03-05T06:02:29.192627Z",
"schema_version": "1.4.0"
}
},
"namespaces": {
"cve.org": {
"CVE_data_meta": {
"ASSIGNER": "security-advisories@github.com",
"ID": "CVE-2024-28108",
"STATE": "PUBLIC"
},
"affects": {
"vendor": {
"vendor_data": [
{
"product": {
"product_data": [
{
"product_name": "phpMyFAQ",
"version": {
"version_data": [
{
"version_affected": "=",
"version_value": "3.2.5"
}
]
}
}
]
},
"vendor_name": "thorsten"
}
]
}
},
"data_format": "MITRE",
"data_type": "CVE",
"data_version": "4.0",
"description": {
"description_data": [
{
"lang": "eng",
"value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. Due to insufficient validation on the `contentLink` parameter, it is possible for unauthenticated users to inject HTML code to the page which might affect other users. _Also, requires that adding new FAQs is allowed for guests and that the admin doesn\u0027t check the content of a newly added FAQ._ This vulnerability is fixed in 3.2.6."
}
]
},
"impact": {
"cvss": [
{
"attackComplexity": "HIGH",
"attackVector": "NETWORK",
"availabilityImpact": "NONE",
"baseScore": 4.7,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "NONE",
"scope": "CHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:C/C:L/I:L/A:N",
"version": "3.1"
}
]
},
"problemtype": {
"problemtype_data": [
{
"description": [
{
"cweId": "CWE-79",
"lang": "eng",
"value": "CWE-79: Improper Neutralization of Input During Web Page Generation (\u0027Cross-site Scripting\u0027)"
}
]
},
{
"description": [
{
"cweId": "CWE-80",
"lang": "eng",
"value": "CWE-80: Improper Neutralization of Script-Related HTML Tags in a Web Page (Basic XSS)"
}
]
}
]
},
"references": {
"reference_data": [
{
"name": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh",
"refsource": "MISC",
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh"
},
{
"name": "https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634",
"refsource": "MISC",
"url": "https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634"
}
]
},
"source": {
"advisory": "GHSA-48vw-jpf8-hwqh",
"discovery": "UNKNOWN"
}
},
"nvd.nist.gov": {
"cve": {
"descriptions": [
{
"lang": "en",
"value": "phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. Due to insufficient validation on the `contentLink` parameter, it is possible for unauthenticated users to inject HTML code to the page which might affect other users. _Also, requires that adding new FAQs is allowed for guests and that the admin doesn\u0027t check the content of a newly added FAQ._ This vulnerability is fixed in 3.2.6."
},
{
"lang": "es",
"value": "phpMyFAQ es una aplicaci\u00f3n web de preguntas frecuentes de c\u00f3digo abierto para PHP 8.1+ y MySQL, PostgreSQL y otras bases de datos. Debido a una validaci\u00f3n insuficiente del par\u00e1metro \"contentLink\", es posible que usuarios no autenticados inyecten c\u00f3digo HTML en la p\u00e1gina, lo que podr\u00eda afectar a otros usuarios. _Adem\u00e1s, requiere que se permita agregar nuevas preguntas frecuentes a los invitados y que el administrador no verifique el contenido de las preguntas frecuentes reci\u00e9n agregadas._ Esta vulnerabilidad se corrigi\u00f3 en 3.2.6."
}
],
"id": "CVE-2024-28108",
"lastModified": "2024-03-26T12:55:05.010",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "HIGH",
"attackVector": "NETWORK",
"availabilityImpact": "NONE",
"baseScore": 4.7,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "NONE",
"scope": "CHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:C/C:L/I:L/A:N",
"version": "3.1"
},
"exploitabilityScore": 1.6,
"impactScore": 2.7,
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
},
"published": "2024-03-25T19:15:58.700",
"references": [
{
"source": "security-advisories@github.com",
"url": "https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634"
},
{
"source": "security-advisories@github.com",
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Awaiting Analysis",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-79"
},
{
"lang": "en",
"value": "CWE-80"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
}
}
}
}
Sightings
| Author | Source | Type | Date | Other |
|---|
Nomenclature
- Seen: The vulnerability was mentioned, discussed, or observed by the user.
- Confirmed: The vulnerability has been validated from an analyst's perspective.
- Published Proof of Concept: A public proof of concept is available for this vulnerability.
- Exploited: The vulnerability was observed as exploited by the user who reported the sighting.
- Patched: The vulnerability was observed as successfully patched by the user who reported the sighting.
- Not exploited: The vulnerability was not observed as exploited by the user who reported the sighting.
- Not confirmed: The user expressed doubt about the validity of the vulnerability.
- Not patched: The vulnerability was not observed as successfully patched by the user who reported the sighting.
The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.
Browse all ATT&CK techniques and the vulnerabilities related to each.
Related by attack behaviour
Vulnerabilities whose description is nearest to this one in the vector space of the CIRCL/vulnerability-attack-technique-biencoder model. This is a similarity search over the bi-encoder space (plain cosine), not a classification, and it has no measured accuracy.