CVE-2026-52796 (GCVE-0-2026-52796)
Vulnerability from cvelistv5 – Published: 2026-06-24 20:13 – Updated: 2026-06-25 20:10
VLAI
EPSS
VEX
Title
Gogs: DoS in rendering issue index pattern
Summary
Gogs is an open source self-hosted Git service. Prior to 0.14.3, specially crafted issue index pattern can cause a panic when rendering, resulting in denial of service. In internal/markup/markup.go, RenderIssueIndexPattern renders the issue index pattern to a link using com.Expand, which is not safe: when the configured pattern contains an opening brace { but no closing brace }, strings.Index(template, "}") returns -1 and the subsequent slice template[:-1] triggers a panic. Once such a pattern is set, any page in the affected repository that contains an issue index reference such as #1 becomes unavailable. This vulnerability is fixed in 0.14.3.
Severity
SSVC
Exploitation: poc
Automatable: no
Technical Impact: partial
CISA Coordinator · CISA-ADP (v2.0.3)
Decision recorded 2026-06-25 20:10 UTC
CWE
- CWE-1336 - Improper Neutralization of Special Elements Used in a Template Engine
Assigner
References
1 reference
| URL | Tags |
|---|---|
| https://github.com/gogs/gogs/security/advisories/… | x_refsource_CONFIRM |
{
  "containers": {
    "adp": [
      {
        "metrics": [
          {
            "other": {
              "content": {
                "id": "CVE-2026-52796",
                "options": [
                  {
                    "Exploitation": "poc"
                  },
                  {
                    "Automatable": "no"
                  },
                  {
                    "Technical Impact": "partial"
                  }
                ],
                "role": "CISA Coordinator",
                "timestamp": "2026-06-25T20:10:04.777866Z",
                "version": "2.0.3"
              },
              "type": "ssvc"
            }
          }
        ],
        "providerMetadata": {
          "dateUpdated": "2026-06-25T20:10:28.834Z",
          "orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
          "shortName": "CISA-ADP"
        },
        "references": [
          {
            "tags": [
              "exploit"
            ],
            "url": "https://github.com/gogs/gogs/security/advisories/GHSA-4j89-2c4f-44c6"
          }
        ],
        "title": "CISA ADP Vulnrichment"
      }
    ],
    "cna": {
      "affected": [
        {
          "product": "gogs",
          "vendor": "gogs",
          "versions": [
            {
              "status": "affected",
              "version": "\u003c 0.14.3"
            }
          ]
        }
      ],
      "descriptions": [
        {
          "lang": "en",
          "value": "Gogs is an open source self-hosted Git service. Prior to 0.14.3, specially crafted issue index pattern can cause a panic when rendering, resulting in denial of service. In internal/markup/markup.go, RenderIssueIndexPattern renders the issue index pattern to a link using com.Expand, which is not safe: when the configured pattern contains an opening brace { but no closing brace }, strings.Index(template, \"}\") returns -1 and the subsequent slice template[:-1] triggers a panic. Once such a pattern is set, any page in the affected repository that contains an issue index reference such as #1 becomes unavailable. This vulnerability is fixed in 0.14.3."
        }
      ],
      "metrics": [
        {
          "cvssV3_1": {
            "attackComplexity": "LOW",
            "attackVector": "NETWORK",
            "availabilityImpact": "LOW",
            "baseScore": 3.5,
            "baseSeverity": "LOW",
            "confidentialityImpact": "NONE",
            "integrityImpact": "NONE",
            "privilegesRequired": "LOW",
            "scope": "UNCHANGED",
            "userInteraction": "REQUIRED",
            "vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:N/A:L",
            "version": "3.1"
          }
        }
      ],
      "problemTypes": [
        {
          "descriptions": [
            {
              "cweId": "CWE-1336",
              "description": "CWE-1336: Improper Neutralization of Special Elements Used in a Template Engine",
              "lang": "en",
              "type": "CWE"
            }
          ]
        }
      ],
      "providerMetadata": {
        "dateUpdated": "2026-06-24T20:13:11.884Z",
        "orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
        "shortName": "GitHub_M"
      },
      "references": [
        {
          "name": "https://github.com/gogs/gogs/security/advisories/GHSA-4j89-2c4f-44c6",
          "tags": [
            "x_refsource_CONFIRM"
          ],
          "url": "https://github.com/gogs/gogs/security/advisories/GHSA-4j89-2c4f-44c6"
        }
      ],
      "source": {
        "advisory": "GHSA-4j89-2c4f-44c6",
        "discovery": "UNKNOWN"
      },
      "title": "Gogs: DoS in rendering issue index pattern"
    }
  },
  "cveMetadata": {
    "assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
    "assignerShortName": "GitHub_M",
    "cveId": "CVE-2026-52796",
    "datePublished": "2026-06-24T20:13:11.884Z",
    "dateReserved": "2026-06-08T18:02:19.731Z",
    "dateUpdated": "2026-06-25T20:10:28.834Z",
    "state": "PUBLISHED"
  },
  "dataType": "CVE_RECORD",
  "dataVersion": "5.2",
  "vulnerability-lookup:meta": {
    "epss": {
      "cve": "CVE-2026-52796",
      "date": "2026-09-19",
      "epss": "0.00284",
      "percentile": "0.21208"
    },
    "nvd": {
      "cve": {
        "affected": [
          {
            "affectedData": [
              {
                "product": "gogs",
                "vendor": "gogs",
                "versions": [
                  {
                    "status": "affected",
                    "version": "\u003c 0.14.3"
                  }
                ]
              }
            ],
            "source": "security-advisories@github.com"
          }
        ],
        "cveTags": [],
        "descriptions": [
          {
            "lang": "en",
            "value": "Gogs is an open source self-hosted Git service. Prior to 0.14.3, specially crafted issue index pattern can cause a panic when rendering, resulting in denial of service. In internal/markup/markup.go, RenderIssueIndexPattern renders the issue index pattern to a link using com.Expand, which is not safe: when the configured pattern contains an opening brace { but no closing brace }, strings.Index(template, \"}\") returns -1 and the subsequent slice template[:-1] triggers a panic. Once such a pattern is set, any page in the affected repository that contains an issue index reference such as #1 becomes unavailable. This vulnerability is fixed in 0.14.3."
          }
        ],
        "id": "CVE-2026-52796",
        "lastModified": "2026-06-25T21:16:27.133",
        "metrics": {
          "cvssMetricV31": [
            {
              "cvssData": {
                "attackComplexity": "LOW",
                "attackVector": "NETWORK",
                "availabilityImpact": "LOW",
                "baseScore": 3.5,
                "baseSeverity": "LOW",
                "confidentialityImpact": "NONE",
                "integrityImpact": "NONE",
                "privilegesRequired": "LOW",
                "scope": "UNCHANGED",
                "userInteraction": "REQUIRED",
                "vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:N/A:L",
                "version": "3.1"
              },
              "exploitabilityScore": 2.1,
              "impactScore": 1.4,
              "source": "security-advisories@github.com",
              "type": "Secondary"
            }
          ],
          "ssvcV203": [
            {
              "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
              "ssvcData": {
                "id": "CVE-2026-52796",
                "options": [
                  {
                    "exploitation": "poc"
                  },
                  {
                    "automatable": "no"
                  },
                  {
                    "technicalImpact": "partial"
                  }
                ],
                "role": "CISA Coordinator",
                "timestamp": "2026-06-25T20:10:04.777866Z",
                "version": "2.0.3"
              }
            }
          ]
        },
        "published": "2026-06-24T21:16:55.270",
        "references": [
          {
            "source": "security-advisories@github.com",
            "url": "https://github.com/gogs/gogs/security/advisories/GHSA-4j89-2c4f-44c6"
          },
          {
            "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
            "url": "https://github.com/gogs/gogs/security/advisories/GHSA-4j89-2c4f-44c6"
          }
        ],
        "sourceIdentifier": "security-advisories@github.com",
        "vulnStatus": "Deferred",
        "weaknesses": [
          {
            "description": [
              {
                "lang": "en",
                "value": "CWE-1336"
              }
            ],
            "source": "security-advisories@github.com",
            "type": "Secondary"
          }
        ]
      }
    },
    "suse_vex": {
      "aggregate_severity": "low",
      "current_release_date": "2026-07-30T16:42:36Z",
      "cve": "CVE-2026-52796",
      "id": "CVE-2026-52796",
      "initial_release_date": "2026-07-30T16:42:36Z",
      "source": "SUSE CSAF VEX",
      "status": "interim",
      "title": "SUSE CVE CVE-2026-52796",
      "url": "https://ftp.suse.com/pub/projects/security/csaf-vex/cve-2026-52796.json",
      "version": "2"
    },
    "vulnrichment": {
      "containers": {
        "adp": [
          {
            "metrics": [
              {
                "other": {
                  "content": {
                    "id": "CVE-2026-52796",
                    "options": [
                      {
                        "Exploitation": "poc"
                      },
                      {
                        "Automatable": "no"
                      },
                      {
                        "Technical Impact": "partial"
                      }
                    ],
                    "role": "CISA Coordinator",
                    "timestamp": "2026-06-25T20:10:04.777866Z",
                    "version": "2.0.3"
                  },
                  "type": "ssvc"
                }
              }
            ],
            "providerMetadata": {
              "dateUpdated": "2026-06-25T20:10:16.768Z",
              "orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
              "shortName": "CISA-ADP"
            },
            "references": [
              {
                "tags": [
                  "exploit"
                ],
                "url": "https://github.com/gogs/gogs/security/advisories/GHSA-4j89-2c4f-44c6"
              }
            ],
            "title": "CISA ADP Vulnrichment"
          }
        ],
        "cna": {
          "affected": [
            {
              "product": "gogs",
              "vendor": "gogs",
              "versions": [
                {
                  "status": "affected",
                  "version": "\u003c 0.14.3"
                }
              ]
            }
          ],
          "descriptions": [
            {
              "lang": "en",
              "value": "Gogs is an open source self-hosted Git service. Prior to 0.14.3, specially crafted issue index pattern can cause a panic when rendering, resulting in denial of service. In internal/markup/markup.go, RenderIssueIndexPattern renders the issue index pattern to a link using com.Expand, which is not safe: when the configured pattern contains an opening brace { but no closing brace }, strings.Index(template, \"}\") returns -1 and the subsequent slice template[:-1] triggers a panic. Once such a pattern is set, any page in the affected repository that contains an issue index reference such as #1 becomes unavailable. This vulnerability is fixed in 0.14.3."
            }
          ],
          "metrics": [
            {
              "cvssV3_1": {
                "attackComplexity": "LOW",
                "attackVector": "NETWORK",
                "availabilityImpact": "LOW",
                "baseScore": 3.5,
                "baseSeverity": "LOW",
                "confidentialityImpact": "NONE",
                "integrityImpact": "NONE",
                "privilegesRequired": "LOW",
                "scope": "UNCHANGED",
                "userInteraction": "REQUIRED",
                "vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:N/A:L",
                "version": "3.1"
              }
            }
          ],
          "problemTypes": [
            {
              "descriptions": [
                {
                  "cweId": "CWE-1336",
                  "description": "CWE-1336: Improper Neutralization of Special Elements Used in a Template Engine",
                  "lang": "en",
                  "type": "CWE"
                }
              ]
            }
          ],
          "providerMetadata": {
            "dateUpdated": "2026-06-24T20:13:11.884Z",
            "orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
            "shortName": "GitHub_M"
          },
          "references": [
            {
              "name": "https://github.com/gogs/gogs/security/advisories/GHSA-4j89-2c4f-44c6",
              "tags": [
                "x_refsource_CONFIRM"
              ],
              "url": "https://github.com/gogs/gogs/security/advisories/GHSA-4j89-2c4f-44c6"
            }
          ],
          "source": {
            "advisory": "GHSA-4j89-2c4f-44c6",
            "discovery": "UNKNOWN"
          },
          "title": "Gogs: DoS in rendering issue index pattern"
        }
      },
      "cveMetadata": {
        "assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
        "assignerShortName": "GitHub_M",
        "cveId": "CVE-2026-52796",
        "datePublished": "2026-06-24T20:13:11.884Z",
        "dateReserved": "2026-06-08T18:02:19.731Z",
        "dateUpdated": "2026-06-24T20:13:11.884Z",
        "state": "PUBLISHED"
      },
      "dataType": "CVE_RECORD",
      "dataVersion": "5.2"
    }
  }
}
FKIE_CVE-2026-52796
Vulnerability from fkie_nvd - Published: 2026-06-24 21:16 - Updated: 2026-06-25 21:16
Severity
Summary
Gogs is an open source self-hosted Git service. Prior to 0.14.3, specially crafted issue index pattern can cause a panic when rendering, resulting in denial of service. In internal/markup/markup.go, RenderIssueIndexPattern renders the issue index pattern to a link using com.Expand, which is not safe: when the configured pattern contains an opening brace { but no closing brace }, strings.Index(template, "}") returns -1 and the subsequent slice template[:-1] triggers a panic. Once such a pattern is set, any page in the affected repository that contains an issue index reference such as #1 becomes unavailable. This vulnerability is fixed in 0.14.3.
References
Impacted products
| Vendor | Product | Version |
|---|
{
  "affected": [
    {
      "affectedData": [
        {
          "product": "gogs",
          "vendor": "gogs",
          "versions": [
            {
              "status": "affected",
              "version": "\u003c 0.14.3"
            }
          ]
        }
      ],
      "source": "security-advisories@github.com"
    }
  ],
  "cveTags": [],
  "descriptions": [
    {
      "lang": "en",
      "value": "Gogs is an open source self-hosted Git service. Prior to 0.14.3, specially crafted issue index pattern can cause a panic when rendering, resulting in denial of service. In internal/markup/markup.go, RenderIssueIndexPattern renders the issue index pattern to a link using com.Expand, which is not safe: when the configured pattern contains an opening brace { but no closing brace }, strings.Index(template, \"}\") returns -1 and the subsequent slice template[:-1] triggers a panic. Once such a pattern is set, any page in the affected repository that contains an issue index reference such as #1 becomes unavailable. This vulnerability is fixed in 0.14.3."
    }
  ],
  "id": "CVE-2026-52796",
  "lastModified": "2026-06-25T21:16:27.133",
  "metrics": {
    "cvssMetricV31": [
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "LOW",
          "baseScore": 3.5,
          "baseSeverity": "LOW",
          "confidentialityImpact": "NONE",
          "integrityImpact": "NONE",
          "privilegesRequired": "LOW",
          "scope": "UNCHANGED",
          "userInteraction": "REQUIRED",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:N/A:L",
          "version": "3.1"
        },
        "exploitabilityScore": 2.1,
        "impactScore": 1.4,
        "source": "security-advisories@github.com",
        "type": "Secondary"
      }
    ],
    "ssvcV203": [
      {
        "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
        "ssvcData": {
          "id": "CVE-2026-52796",
          "options": [
            {
              "exploitation": "poc"
            },
            {
              "automatable": "no"
            },
            {
              "technicalImpact": "partial"
            }
          ],
          "role": "CISA Coordinator",
          "timestamp": "2026-06-25T20:10:04.777866Z",
          "version": "2.0.3"
        }
      }
    ]
  },
  "published": "2026-06-24T21:16:55.270",
  "references": [
    {
      "source": "security-advisories@github.com",
      "url": "https://github.com/gogs/gogs/security/advisories/GHSA-4j89-2c4f-44c6"
    },
    {
      "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
      "url": "https://github.com/gogs/gogs/security/advisories/GHSA-4j89-2c4f-44c6"
    }
  ],
  "sourceIdentifier": "security-advisories@github.com",
  "vulnStatus": "Deferred",
  "weaknesses": [
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-1336"
        }
      ],
      "source": "security-advisories@github.com",
      "type": "Secondary"
    }
  ]
}
GHSA-4J89-2C4F-44C6
Vulnerability from github – Published: 2026-06-22 23:58 – Updated: 2026-07-21 13:17
VLAI
Summary
Gogs has DoS in rendering issue index pattern
Details
Summary
Special template of issue index pattern may cause panic.
Details
in internal/markup/markup.go
link = fmt.Sprintf(`<a href="%s">%s</a>`, com.Expand(metas["format"], metas), m)
Issue index pattern is rendered to link with com.Expand.
However, com.Expand is not safe.
i = strings.Index(template, "}")
if s, ok := match[template[:i]]; ok {
when { is found but } not found, i comes to 1, template[:-1] will be called, and then panicked
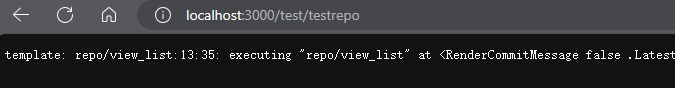
finally, all pages than contains issue index are unavailable.
PoC
- set issue index pattern as follow
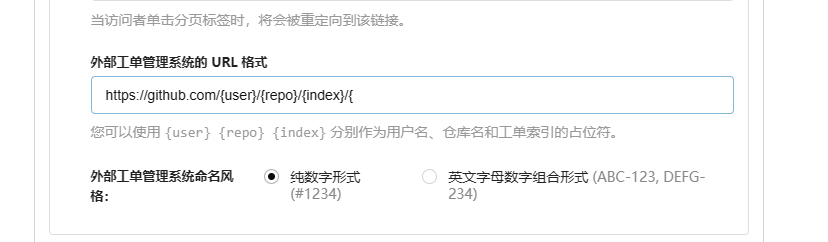
- add a commit which point to an issue in its msg
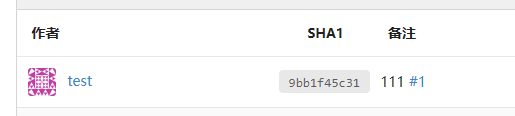
using #1 above
Impact
DoS that cause part of pages of the specify repo unavailable.
Severity
{
"affected": [
{
"database_specific": {
"last_known_affected_version_range": "\u003c= 0.14.2"
},
"package": {
"ecosystem": "Go",
"name": "gogs.io/gogs"
},
"ranges": [
{
"events": [
{
"introduced": "0"
},
{
"fixed": "0.14.3"
}
],
"type": "ECOSYSTEM"
}
]
}
],
"aliases": [
"CVE-2026-52796"
],
"database_specific": {
"cwe_ids": [
"CWE-1336"
],
"github_reviewed": true,
"github_reviewed_at": "2026-06-22T23:58:17Z",
"nvd_published_at": "2026-06-24T21:16:55Z",
"severity": "LOW"
},
"details": "### Summary\nSpecial template of issue index pattern may cause panic.\n\n### Details\n\nin internal/markup/markup.go\n\n```go\nlink = fmt.Sprintf(`\u003ca href=\"%s\"\u003e%s\u003c/a\u003e`, com.Expand(metas[\"format\"], metas), m)\n```\n\nIssue index pattern is rendered to link with `com.Expand`.\n\nHowever, `com.Expand` is not safe.\n\n```go\ni = strings.Index(template, \"}\")\nif s, ok := match[template[:i]]; ok {\n```\n\nwhen `{` is found but `}` not found, i comes to 1, template[:-1] will be called, and then panicked\n\n\n\nfinally, all pages than contains issue index are unavailable.\n\n### PoC\n\n1. set issue index pattern as follow\n\n\n\n2. add a commit which point to an issue in its msg\n\n\n\nusing `#1` above\n\n### Impact\n\nDoS that cause part of pages of the specify repo unavailable.",
"id": "GHSA-4j89-2c4f-44c6",
"modified": "2026-07-21T13:17:05Z",
"published": "2026-06-22T23:58:17Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/gogs/gogs/security/advisories/GHSA-4j89-2c4f-44c6"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2026-52796"
},
{
"type": "WEB",
"url": "https://github.com/gogs/gogs/pull/8312"
},
{
"type": "WEB",
"url": "https://github.com/gogs/gogs/commit/0529d95fc39f2b6d2997b19a2a12e24522684722"
},
{
"type": "PACKAGE",
"url": "https://github.com/gogs/gogs"
},
{
"type": "WEB",
"url": "https://github.com/gogs/gogs/releases/tag/v0.14.3"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:N/A:L",
"type": "CVSS_V3"
}
],
"summary": "Gogs has DoS in rendering issue index pattern"
}
Loading…
Loading…
Experimental. This forecast is provided for visualization only and may change without notice. Do not use it for operational decisions.
Forecast uses a logistic model when the trend is rising, or an exponential decay model when the trend is falling. Fitted via linearized least squares.
Sightings
| Author | Source | Type | Date | Other |
|---|
Nomenclature
- Seen: The vulnerability was mentioned, discussed, or observed by the user.
- Confirmed: The vulnerability has been validated from an analyst's perspective.
- Published Proof of Concept: A public proof of concept is available for this vulnerability.
- Exploited: The vulnerability was observed as exploited by the user who reported the sighting.
- Patched: The vulnerability was observed as successfully patched by the user who reported the sighting.
- Not exploited: The vulnerability was not observed as exploited by the user who reported the sighting.
- Not confirmed: The user expressed doubt about the validity of the vulnerability.
- Not patched: The vulnerability was not observed as successfully patched by the user who reported the sighting.
Loading…
The MITRE ATT&CK techniques below are AI-generated suggestions, inferred from the description of the
vulnerability by the CIRCL/vulnerability-attack-technique-classification-roberta-base
model, served locally by ML-Gateway.
They have not been verified by an analyst and are provided for guidance only.
The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.
Browse all ATT&CK techniques and the vulnerabilities related to each.
The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.
Browse all ATT&CK techniques and the vulnerabilities related to each.
Loading…
Related by attack behaviour
Vulnerabilities whose description is nearest to this one in the vector space of the CIRCL/vulnerability-attack-technique-biencoder model. This is a similarity search over the bi-encoder space (plain cosine), not a classification, and it has no measured accuracy.
Loading…